Former Ledger employee falls victim to phishing attack, causing Web3 players to be fooled last night.
Last night, hackers gave Web3 users a little break.
On December 14th at 20:00, Sushi's Chief Technology Officer @MatthewLilley issued a warning on social media, advising users not to interact with any dApps until further notice. A commonly used Web3 connector appears to have been compromised, allowing for the injection of malicious code that could affect numerous dApps.
Not only the front-end of Zapper and Sushi were affected, but according to statistics, over 100 dapps were impacted.
This is related to the software library of hardware wallet provider Ledger. The reason is that LedgerHQ/connect-kit loads JavaScript from a CDN, and their CDN account has been compromised, injecting malicious JavaScript into multiple dApps. Many dApps rely on the poisoned code library of Ledger, which has a wide impact.
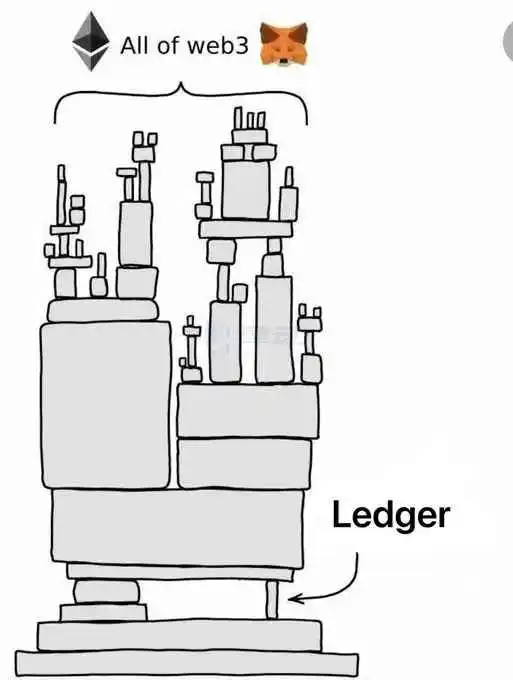
At the reminder of various parties, Web3 users took a short break last night and refrained from conducting on-chain operations temporarily, in order to avoid interacting with the poisoned DApps.
Former employee account leaked, attack team has long been lurking
The founder of SlowMist, Yu Xian, posted on social media that from the code editing page, it can be seen that the Ledger code library attack group began tampering with ledgerhq/connect-kit version 1.1.5, but did not implant malicious code, only wrote some mocking information.
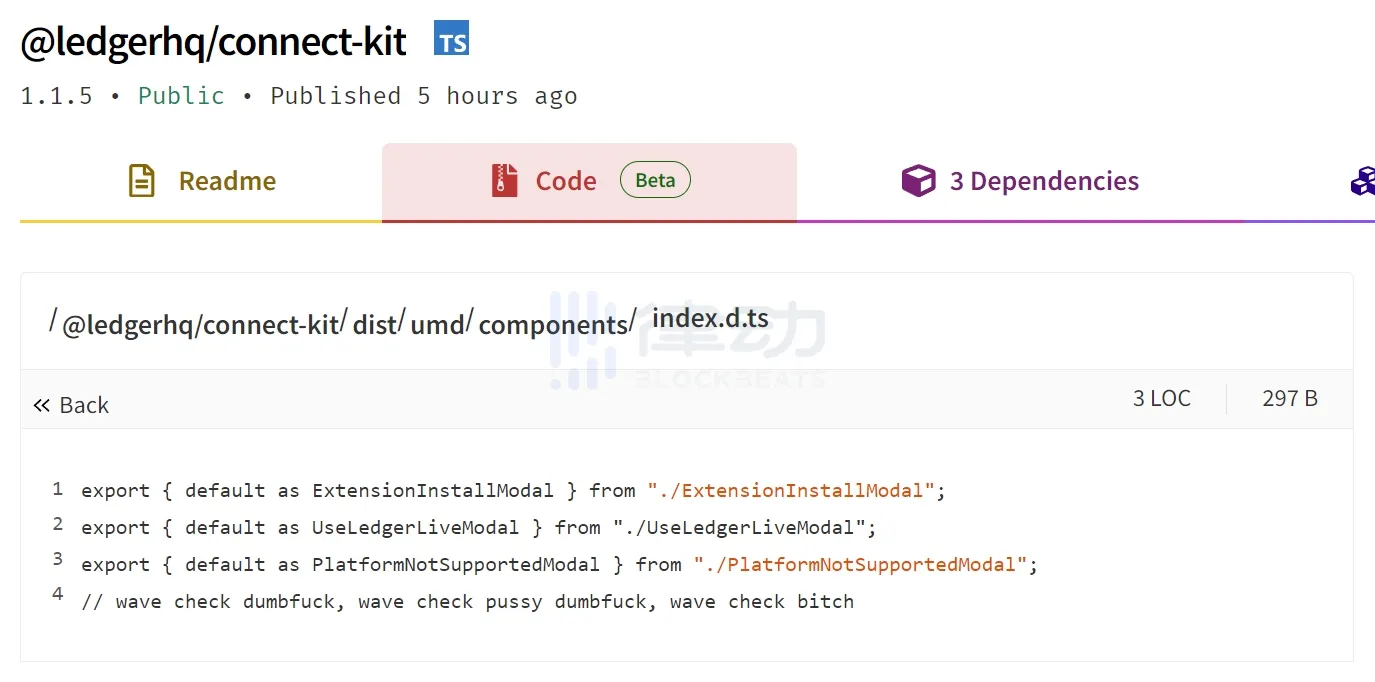
Starting from version 1.1.6, malicious code was implanted, but there may have been some issues, and a version with malicious code, 1.1.7, was subsequently released. Finally, the hacker left a message thanking the Inferno Drainer phishing toolkit, which was announced to have stopped service some time ago.

Currently, Ledger, Walletconnect, and their partners have reported the hacker's wallet. Tether has frozen the attacker's USDT.
Ledger is filing a complaint and cooperating with law enforcement to investigate the attacker, while also analyzing the exploit to prevent future attacks. It is believed that the attacker's address, 0x658729879fca881d9526480b82ae00efc54b5c2d, is under review.
Scope Protocol, jointly created by 0xSentry, posted on social media that the digital traces left by the attacker involved @JunichiSugiura (Jun, former employee of Ledger)'s Gmail account, which may have been compromised.
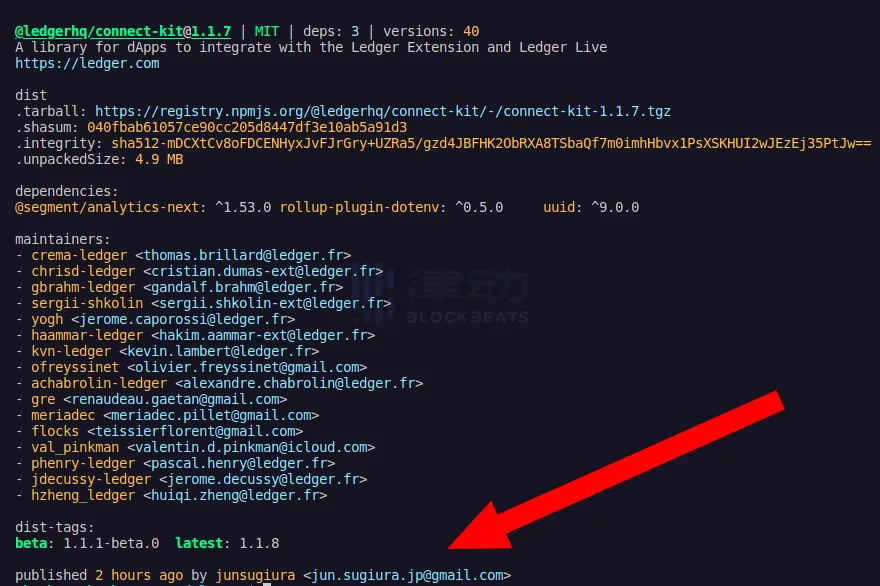
Some developers have suggested that one possible scenario is that Jun's Github account has been compromised and Ledger forgot to revoke his access after he left.
In this so-called "dark forest", such hunters are not uncommon and may occur in the future, so users need to be vigilant.
Although the security issue of the Ledger module ledgerhq/connect-kit has been mitigated, there may be poisoned code residue in the browser cache. This also applies to the cache in the built-in browser of the wallet application. Therefore, it is recommended that all users clear their cache and wait for 24 hours before engaging in wallet activities.
Also, it is important to increase vigilance towards signed transactions. In the world of blockchain, unpredictable security threats can occur, so carefully examining transaction content is crucial.
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia

 Related Articles