If the FTX wallet anomaly is a hacker attack, it needs to satisfy at least these points
Original article by KOL CryptoNerdCn
On November 12, FTX and FTX US collected large assets at an address beginning with 0x59a, which was mistaken for the address of FTX liquidator after FTX announced to file for bankruptcy reorganization. However, the address raises questions about a series of dynamics up the chain. Later, FTX said in its Telegram community that FTX had been hacked and its assets had been stolen. KOL CryptoNerdCn is doubtful about this event. If FTX hack is true, what conditions do you need? The following is reproduced by BlockBeats:
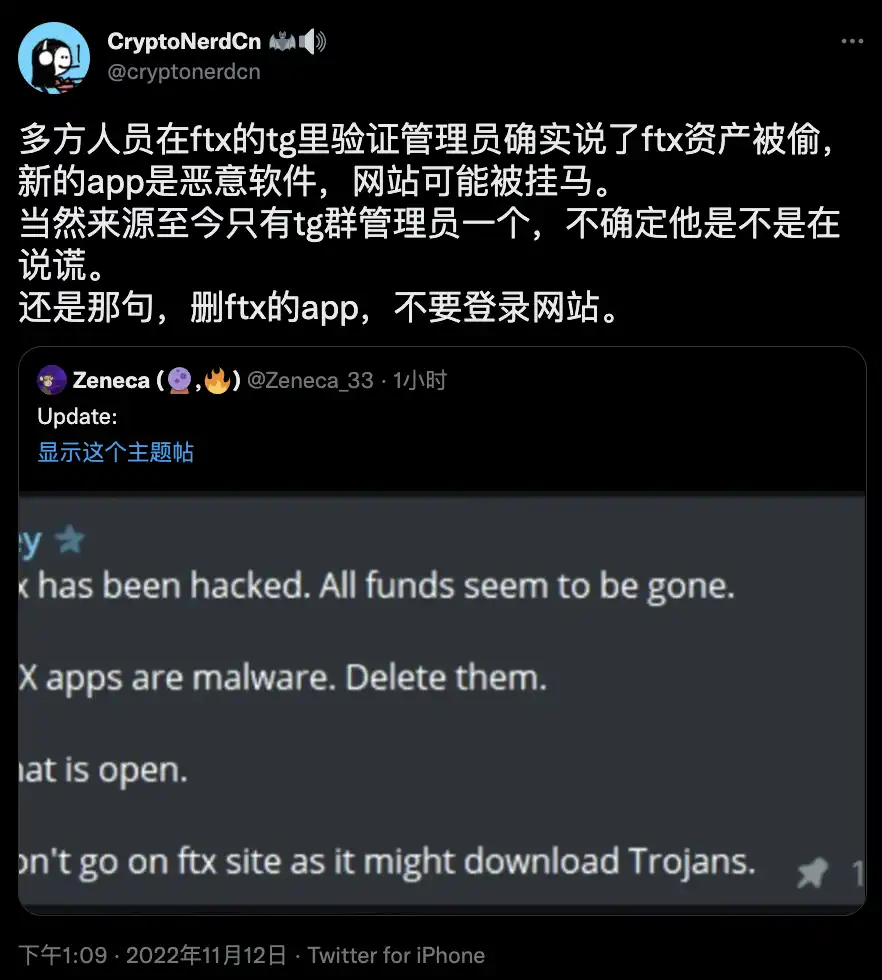
多方人员在 FTX 的 TG 里验证管理员确实说了 FTX 资产被偷,新的 App 是恶意软件,网站可能被挂马。 当然来源至今只有TG 群管理员一个,不确定他是不是在说谎。 还是那句,删 FTX 的 App,不要登录网站。
The jury is still out. Is SBF inside the house? Or did some of the employees do evil and try to escape? Or an attacker from the outside? It's all possible.
But it is a great coincidence that the same colleagues who were able to attack assets on the chain and update FTX's App as malware were able to break into FTX's website. A hacker would need to get his hands on much more than a private key and password that should be closely guarded, not to mention the 2FA verification process that might be involved.
For example, updating an App in the mobile market, even one like Android, which is much more convenient than ios, requires you to get the apk signature key before you can sign and publish the new apk.
网站要简单一点,但同样需要你有更改服务器里的内容的权限。如果不是现有权限账号泄漏,那就是攻击者攻进去后给自己提权。 上面两者拿下任意一个都不是容易的事。
可以看出除非 FTX 把以下三种信息放在同一个地方,包括:钱包密钥;App 的签名密钥;有更改服务器权限的账户名和口令。不然黑客是很难做到同时对三者进行攻击的。 (网站还有可能是前端缺陷被挂马,但时机太巧了)。
Link to original article
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia

 Related Articles