Former FTX employee reveals How client money went to Alameda without audit?
Original title: Former FTX Employee Reveals How Money Moved between Client, CHO and Alameda without Audit Detection
Original article by Yung Dot
Guo Qianwen, ChainCatcher
I wasn't going to share any of this, but when I had the opportunity to share it anonymously with Mario Nawfal, I decided to. But instead of accepting paystubs/ids, digital ids, emails, wallet faxes as verification, Mario wants a LinkedIn connection?
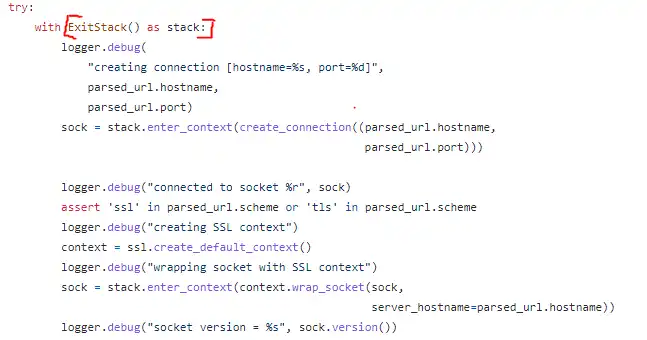
As a former FTX employee, I can talk about how funds were successfully moved between customer, CHO and Alameda wallets without being detected by auditors. The entire hack was made possible by the elx trapdoor, which SBF launched about nine months ago and is also showing up in public beta.
As the name suggests, this feature allows Sam to use elx to send fraudulent logger messages to auditors through negative flux when they want to query the database. It's useful for Sam to add this feature. It's a very common feature, but he's good with these little things.
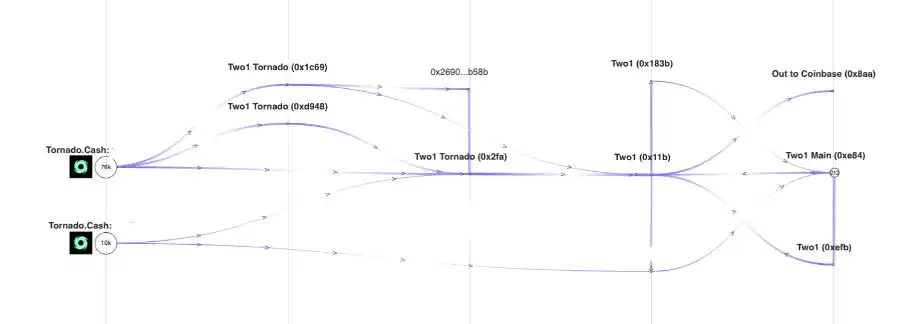
The log is resolved to the wallet 0x1c69, which then starts glm The transfer function of; Here is just an example showing how to wash away 76k+10k ETH via Tornado. To the auditor, there is nothing unusual about the log returning from the server side, and the money on the front end appears safe.
On FTX APP Our task was to design additions (Augmented deficit decoders, for short) to help confuse and protect the code base, which later appeared to have been used maliciously to cover up wrongdoing by executives.
When & have spent When the FTT reaches 200wma, these decoders are used to make it in LTF With each rally, the FTT got stronger, but after high-frequency trading (HTF), it couldn't hold on, and that was the beginning of the collapse. My team was "fired" for being unfit -- even after we came up with the information to support it. After the FTT mix-up. Eg. We spent it. The ADD of years of research is now being used in fraud and our wishes are not being respected.
My main question is how Rupert managed to pick himself clean during the whole process. Sam, Gary and Caroline have been making headlines, but multiple signatories. Rupert Calloway, a long-time SBF friend and MIT hacker whose name was revealed yesterday by Mario Nawfal, did not appear in the public eye.
Rupert may never, ever go to jail, because signing multiple signatures is hardly a crime, and he could argue that he was acting under duress. But what is surprising is how $783 million needed to be signed by four people, none of whom seem to have known about it, suddenly disappeared.
Rupert Dox The wallet (thanks again to Mario Nawfal's Space) currently holds $6.6 million ETH and seems to be shuffling between various addresses - why on earth?
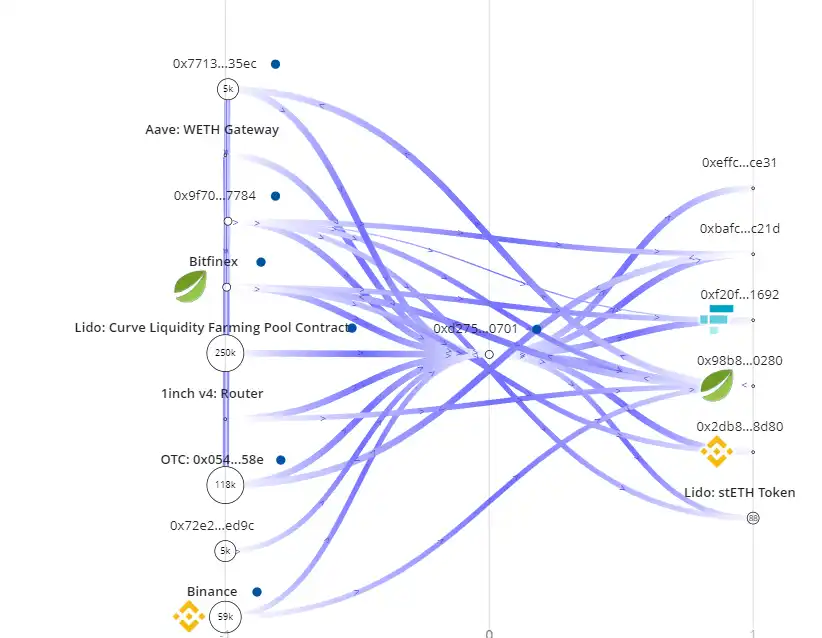
One of them is 0x72. 0x72 happens to have Milady#241. So, who owns it? None other than Caroline. This raises more questions for us to explore.
Link to original article
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia

 Related Articles