Combing the history of ZK technology: Will it be the fertile ground for the next 100 billion applications?
Original title: "We studied the technical history of ZK and found that the next 100 billion applications lie on it"
Original author: Web3 Research Organization R3PO
The focus of the crypto world has experienced multiple changes in Bitcoin, Ethereum, DeFi, NFT, Metaverse and Web3 The only change is the lack of attention to the encryption technology itself. Except for the elliptic curve encryption algorithm (ECC) of Bitcoin, which is still somewhat well-known by the public, other encryption algorithms basically stay in the self-confidence of researchers and developers.
R3PO believes that this is not decentralized enough, which will seriously hinder the further expansion of Web3. Cryptography is the basic piece of blockchain. It should not be mastered by a few people, but should go to a wider field.
R3PO hopes to use a new writing paradigm to explain the meaning of terms, taking into account professionalism and readability, and is committed to providing Investors and project parties discover investment opportunities, entrepreneurial directions and entry points hidden in development, and find undiscovered benefits.
The recent hot zero-knowledge proof technology is still a segmented field that is constantly developing and innovating, but its technology itself is It has a sufficiently broad application scenario, so it is very important to sort out its panorama.
Zero-Knowledge Proof technology (Zero-Knowledge Proof) is not a new concept. So far, after 40 years of development, a variety of models and applications have been born.
Entering the Web3 era, as early as 2017, Vitalik has noticed the potential of using ZK technology on Ethereum, and Recently, Starkware received US$100 million in financing, bringing its total financing amount to 225 million, which means that institutions view ZK technology at the valuation and potential of public chains. This will be a field of long-term fierce competition, and more investment opportunities will be exposed.
Deducting 20 years backward, R3PO believes that the development of ZK has at least the life length of a Jiazi, so it is necessary to describe the entire development process of ZK Tracing back to the source to better clarify its development logic and find potential opportunities for the next step.
The first article in this series will start from zero-knowledge proof, surpass the inherent concept that ZK can only be applied to the L2 field, and bring Everyone has a new systematic cognition.
Zero start: ZK assembly process
1982: If you don’t reveal your wealth, you will be distinguished

For The pursuit of wealth has existed since ancient times. Xiang Yu once said: "Wealth does not return home, it is like a night walk in clothes." But too much wealth will attract people to covet. Is there a way to compare the wealth without revealing the amount How much is the wealth?
In 1982, the later Turing Award winner Yao Qizhi conceived this problem, which is the famous millionaire problem, omitted Its mathematical process, its general operation mode is as follows:
- Alice and Bob choose the numbers i and j that represent their own wealth, and the value range is between 1-10
- Alice performs one-way encryption on i, and sends the encrypted result k to Bob, and Bob gets a new value related to i ;
- Bob will get a new value m after operating on k, and pass it back to Alice At this time, Alice can judge the value of m and i relation.
- This process can continue to be deduced, and the two parties can finally complete the comparison without completing the information disclosure.
Of course, the above process is not comprehensive, but it is enough to illustrate a problem, we can indeed be between the two parties, and without Computation is performed on the premise of exposing information. If two parties are extended to multiple parties and the interval is extended to a larger range, then this is a typical MPC (Secure Multi-party Computation) problem.
The millionaire problem is a starting point for ZK discussions:
- Under the condition of not relying on a third party for evaluation , which examines the direct interaction between two parties or parties.
1985: Zero Knowledge Proof

In 1985, Goldwasser, Micali and Rackoff proposed the Zero-Knowledge Proof model for the first time. To be precise, it is an "interactive zero-knowledge proof" model. On the premise of multiple interactions, ZK technology is used to verify the authenticity and size.
The zero-knowledge here is not completely accurate, take the interaction between Alice and Bob as an example, Alice and Bob can verify each other The prover and the prover, but the information transmitted between the two cannot be related to the amount of wealth itself. The zero knowledge here means that the correlation is zero, rather than no information is transmitted.
Interactive refers to multiple interactions, and this process can be repeated until the correct result is obtained.
So far, the well-known ZK technology has taken the first step to take shape, and all subsequent developments are based on deletions, additions and changes .
1991: Non-interactive zero-knowledge proof
< img src="https://image.blockbeats.cn/upload/2022-09-29/f23e55895347f005d32c8e1c1f5570d22b03ddfd.png?x-oss-process=image/quality,q_50/format,webp">
When the time came to 1991, Manuel Blum, Alfredo Santis, Silvio Micali, and Giuseppe Persiano proposed non-interactive zero-knowledge proofs. The point is to carry out the non-interactive proof process, that is, to verify the authenticity of a theorem and hypothesis without interaction between the two parties. This seems counterintuitive, but there is a wonderful example to illustrate:
- Alice and Bob became mathematicians after they got rich and free. Alice leaves web2 to travel around web3, during which Alice continues ZK research.
- We assume that Alice, when she discovers a proof of a new theorem, can write Bob a postcard proving that she has made new progress in her research.
- This is a non-interactive process, to be precise, it is a one-way interaction: only from Alice to Bob. Even if Bob wanted to answer, he couldn't. Because Alice doesn't have a stable (or predictable) address, she'll move out before any mail can reach her.
- We agree that as long as Bob receives the email, we don't need to check the content of the email to be sure that "Alice has made new progress in research" The proposition is true.
Non-interactive zero-knowledge proof reduces the number of interactions to at most one time, which can realize offline verification and public verification. The former is Rollups It lays the foundation for effectiveness. The latter is coupled with the broadcast mechanism of the blockchain, which can avoid the waste of resources caused by multiple calculations.
So far, the ZK we have seen so far has become a mature theoretical model, but at this time ZK is more about mathematics and cryptography However, after the emergence of Bitcoin, encryption technology + blockchain became the research direction, and ZK is undoubtedly the best among them.
It is worth noting that Satoshi Nakamoto himself did not reject the use of ZK technology in the Bitcoin network. The ZK technology is immature, so the relatively safe ECC algorithm was finally chosen, and ZK itself can be directly applied to the Layer1 blockchain. Zcash, Mina, and the Istanbul upgrade of Ethereum all involve related fields of zero-knowledge proof.
Meeting: SNARK intervenes in the blockchain
< img src="https://image.blockbeats.cn/upload/2022-09-29/35de3f68d946b720643737d20d3bff4549bde785.png?x-oss-process=image/quality,q_50/format,webp">
2010-2014 Zcash: SNARKs (Zero-Knowledge Succinct Non-Interactive Argument of Knowledge) Practical Scenario
< p>After the emergence of the Bitcoin network, security and privacy became people's initial perception of the blockchain. A series of privacy-based public chains and applications have emerged on the market, such as SNARKs used by Zerocash/Zcash, and Bulletproofs (BP) used in Monero.
In 2010, Groth realized the first ZK based on ECC algorithm, O(1) constant level. Also known as ZK-SNARKs or ZK-SNARGs.
- SNARGs: Succinct Non-Interactive Arguments
- SNARKs: Succinct Non-Interactive Arguments of Knowledge
From an application point of view, this improvement lies in the "simple" Succinct function, specifically , SNARK is committed to compressing the size of the information itself. In ZCash, the program circuit is fixed, so the polynomial verification is also fixed, which makes the setting only need to be performed once, and the subsequent transaction can be reused only by changing the input.
In 2013, the Pinocchio protocol improved the efficiency to minutes-level proof and millisecond-level verification time, and the overhead was controlled at 300 bytes Within the scope, this is also the first time that ZK-SNARKs technology has truly landed in the blockchain field.
This proves that ZK technology can play a role in privacy scenarios. R3PO judges that the subsequent privacy route will have the ability to exist independently of L2 Potential, Aztec proved the feasibility of the private DeFi route, and after tornado was sanctioned, financial privacy on the chain is still a strong rigid demand, investment opportunities in this direction have not been widely explored, and it is worth looking forward to.
In addition, the privacy coin project Zerocash has further improved the relevant algorithm, using the optimized zk-SNARKs algorithm of SCIPR Lab. Under theoretical conditions, it is possible to hide the payment source, recipient and amount, and the transaction can be controlled within 1KB, and the verification time is within 6ms.
Mina: Recursive ZK Compressed Data
Mina is different from Ethereum L2. It is a high-performance public chain at L1 level. Its operating node is only 22KB. The reason why it can be so small is that it uses recursion to prove the validity of ZK confirmation Sexuality, that is, each piece of information carries the previous confirmation results.
- Step1: zk-SNARKs proves the validity of the node, only need to save the proof result;
- Step2: Through recursive calls, ensure the correct delivery and retrieval of node validity, without keeping all historical data, to achieve the effect of extreme data compression;
Transfer the validity of the result instead of saving the full node data. This is Mina's proven effective method. In Ethereum L2, ZK-Rollup can package multiple transaction data , complete the proof of validity by one-time settlement, and further deduction, L3 can be superimposed on top of L2, or Dapp applications, these are subdivision tracks that ZK can develop, such as dYdX currently runs on Starkex, and its architecture is based on Starkware The L2 ImmutableX above all proves the use potential of ZK. The value of this track has not yet been fully tapped, and there is still long-term investment value.
So far, all the technical elements involved in ZK-Rollup are basically complete, and we have already equipped enough basic knowledge of ZK, And the following characteristics of ZK can be summarized:
- Non-interactive: no need for multiple verifications, only one verification can be broadcast to the whole network;< /p>
- Zero-knowledge: No need to disclose the characteristics of the information itself, and it can be publicly disseminated on the entire network;
- Knowledge: Knowledge is not public and easy-to-obtain information, it must have unique value, such as economic value, privacy value, etc.;
- Proof: The proof is confirmed by mathematical means, and the safety has been tested by years of research and practice;
If these technical features are combined Looking at it, we can find that ZK is naturally suitable for L2 expansion, and it is not limited to L2. Other applications of ZK technology will continue to be published in the following articles, and you are welcome to continue to pay attention.
Double Dragon Club: STARK will eventually replace SNARK
< br>
ZK-STARK: A seeded player with a development difficulty of 10 years
Comparing the difference between the two, the main reason is that the S in STARK means Scalability, which is aimed at complex use scenarios with larger data, but It is still a technical route in development as a whole.
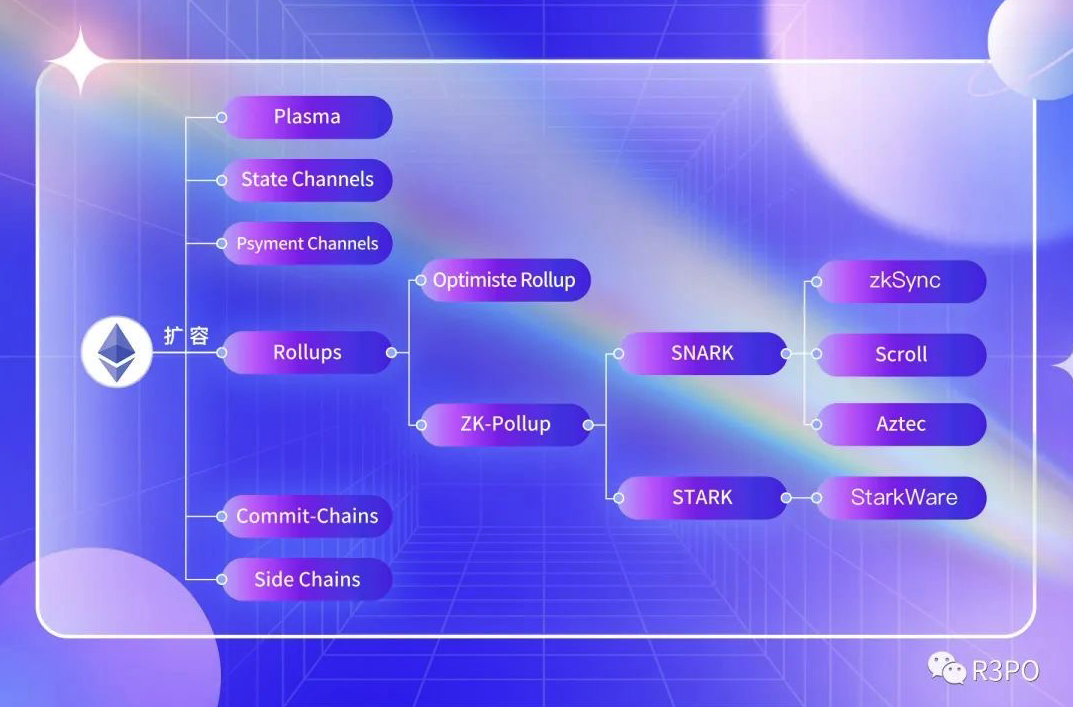
This article does not touch on the differences between the specific L2, but one thing is obvious, in addition to StarkWare, other L2 projects, including zkSync, Aztec, Loopring , Scroll, etc. all adopt the SNARKs technology route.
The reason is that the development of STARK is too difficult. At present, only StarkWare has the ability to conduct self-development, but its benefits are also very Obviously, compared with SNARK, it can carry a larger amount of calculation, and its security will be higher when running large data, such as games, social, NFT and other directions.
Secondly, the STARK route has the characteristics of anti-quantum attack, which may subvert the industry structure in the next ten years. The ECC algorithm used is not fully capable of resisting quantum cracking. If zk-STARKs technology is added, its security will be significantly improved.
The pattern of Ethereum L2 can be summarized, short-term Optimistic Rollup, zk-SNARKs route in 5 years, zk-STARK in 10 years The route will win out in the end.
ZK-Rollup: Data up-drilling, information down-drilling
After the introduction of zk-STARKs, all the technical features of L2 expansion are complete, only the introduction of Rollup is missing. In fact, Rollup uses the verification mechanism of ZK and gets rid of its Demand for data volume: Under the premise that L1 is responsible for consensus and settlement, L2 is responsible for the specific daily operation of the application. Users do not need to interact directly with L1, and their experience will be highly similar to the current App.
Furthermore, after Rollup completes the packaging of information, it will encrypt the verified information into knowledge, and then pass it to L1, to break the impossible triangle of security, decentralization and scalability.
Summary
We start from the millionaire problem, From the MPC problem to the zero-knowledge proof field, due to economic reasons, interactive zero-knowledge proofs are not fully suitable for on-chain activities, and non-interactive zero-knowledge proofs are gradually becoming mainstream.
With the development of Zcash, SNARKs technology is increasingly applied to it, making ZK technology change from a pure cryptography research object to The engineering methods used in the blockchain field play their role in terms of privacy, security, and efficiency.
Ethereum’s expansion scenario has enabled ZK to achieve L2, Rollup technology route to defeat other competitors, and zk-STARKs are also gradually developing Together, it is expected to activate more common usage scenarios such as mining, GameFi, and NFT.
In addition to Ethereum, more and more new models have gradually emerged, such as customizable modular Rollup routes, and For example, Eclipse, which has just completed financing of 15 million US dollars, its roadmap will support the Move language and Solona network, and Scroll, which has completed financing of 30 million US dollars, hopes to establish an EVM equivalent ZK-Rollup.
The driving force behind the new story is the recognition of ZK technology, broadly speaking, ZK is a "big, comprehensive, long-term In the field of "far away", the continuous news of large-scale financing also shows that the market's acceptance of it is gradually increasing, but in general, this is still a new field, even if it is only about its technical route, there are also "introduction" genres , and the investment opportunities among them exist for a long time. Whether it is embedded in the underlying infrastructure or implemented in specific application scenarios, we need to continue to explore.
< p>
Original link
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia

 Related Articles