Defrost Finance hacker returns funds, accused of orchestrating the scam and exiting.
Original Title: "Defrost Finance hacker returns funds, accused of staging the exit scam"
Original Author: Joy, PANews
The big investor Hoi, who lost 12 million dollars due to the theft of Defrost Finance, breathed a sigh of relief last night. Around midnight, he tweeted "It's dawn." Just over an hour ago, Defrost Finance announced that the hackers had returned the funds and they will soon be returned to the users.
Although the ending was ultimately a happy one, the users still labeled it as "self-directed and self-acted".
Defrost Finance has been hacked repeatedly, causing losses of $12 million for major investors
On Christmas Day, December 25th, the Defrost Finance protocol, a native stablecoin project in the Avalanche ecosystem, was found to have another issue. The protocol had fake collateral tokens added and a malicious price oracle was used to liquidate current users, resulting in an estimated loss of over $12 million. Defrost Finance officials stated that they have noticed the emergency situation that occurred in V1 and the team is currently investigating. They urge the community to wait for updates and not to use V1 or V2 for the time being.
Just two days ago, on December 23rd, Defrost FinanceV2 was hit by a flash loan attack by hackers, who profited $173,000. However, V1 was not affected as it did not offer flash loan services.
Later, a user named Hoi tweeted and asked for help within the community, stating that most of the deposits in Defrost Finance were provided by them and that they personally lost 12 million US dollars. Audit firm CertiK has not responded yet and they requested everyone to provide clues.
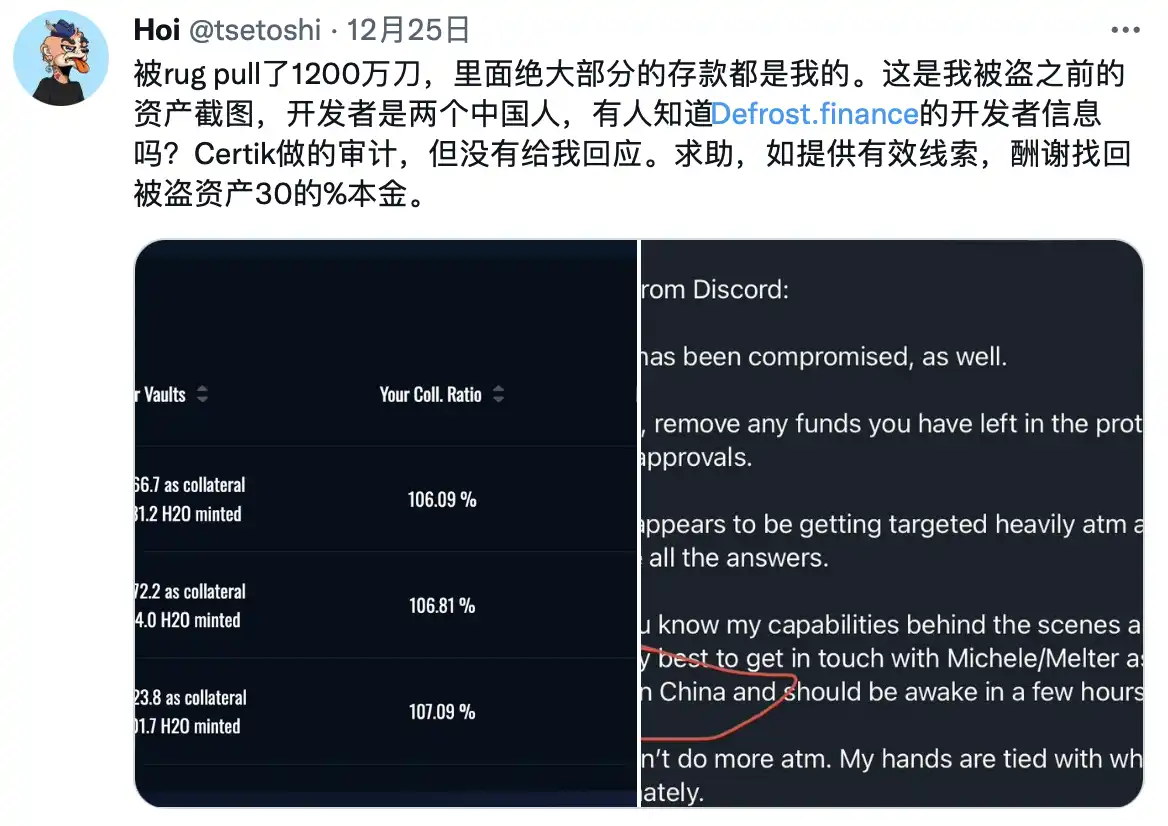
Shortly after, Hoi tweeted again claiming to have obtained some real-name clues from the project party and believed that the project party was stealing from within. This is because all the money in V2 was stolen before V1 was stolen; all the interfaces in V1 were written with anti-reentry, but surprisingly, V2 was not. He speculated that the team had always wanted to make V2 bigger so that they could push the blame onto a third-party attack when attacked, as a third party could trigger it through a flash loan when V2 was attacked. However, there was too little money in V2, which was not enough for the team's appetite. So the next day, they took a risk and used their developer privileges to forcibly change the oracle price, mint coins for themselves, and create a new collateral pool. These operations could not have been triggered by a third party. The development team probably couldn't make money in the bear market, so they just went for it. Anyway, now there is only me, a foolish investor, putting money in this project, and there probably won't be anyone else fighting for their rights, so they stole it.
According to Beosin, a blockchain security audit company, attackers modified the oracle's address through the setOracleAddress function, then used the joinAndMint function to mint 100,000,000 H20 tokens to the address 0x6f31, and finally used a false price oracle to obtain a large amount of USDT through the liquidate function. Subsequently, the stolen funds were transferred to 0x4e22 on Ethereum through cross-chain methods by the attackers. This is consistent with the operation analyzed by Hoi.
黑客返还资金,公链官方、审计公司难辞其咎
Hacker Returns Funds, Public Chain Officials and Audit Companies Cannot Escape Blame
On December 25th at 8pm, Defrost tweeted that the team is willing to negotiate with the hacker and share 20% of the stolen funds in exchange for the return of most of the stolen assets. The specific amount can be negotiated, and they urge the hacker to contact them as soon as possible.
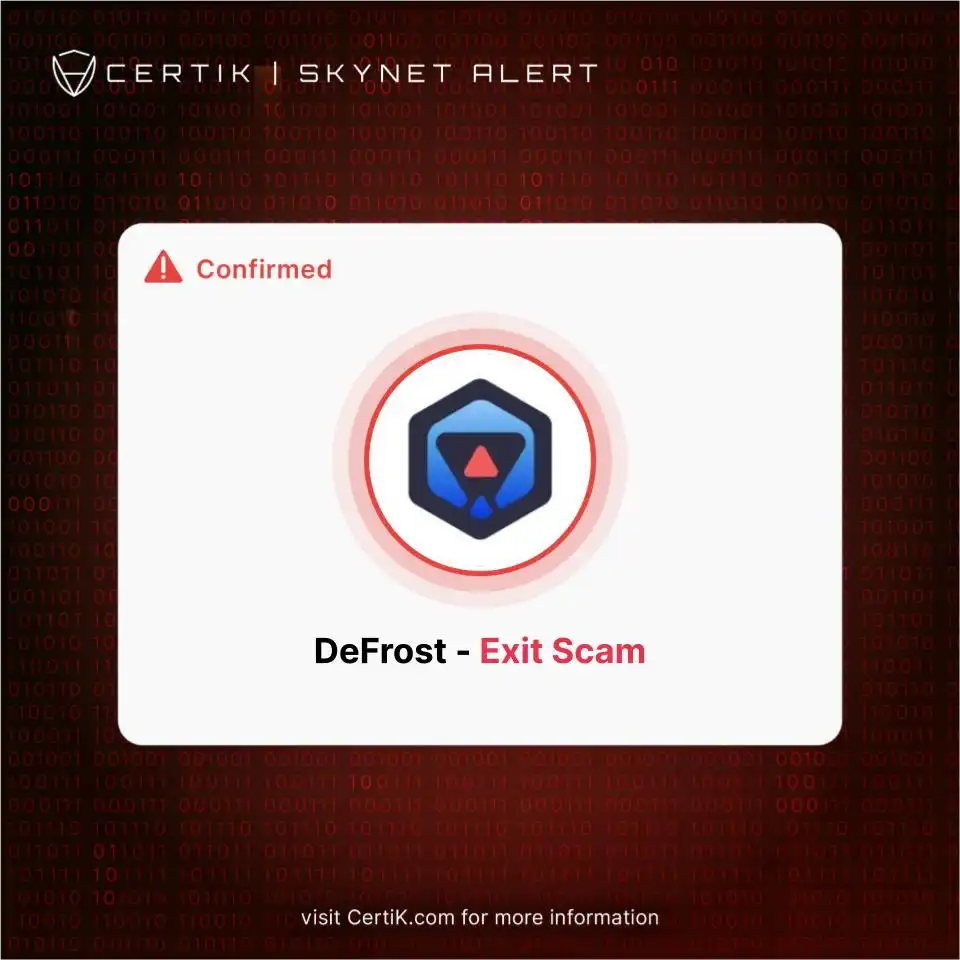
On the afternoon of December 26th, CertiK, the auditing company of Defrost Finance, tweeted that monitoring showed that the Defrost Finance project was an exit scam. CertiK had attempted to contact multiple members of the team but did not receive a response. In addition, CertiK also stated that "the team did not conduct KYC, but we are using all the information we have to assist the authorities." This seems to confirm Defrost's self-destructive behavior.
Perhaps the personal information of "hackers" was obtained, so they chose to quickly return the funds. Defrost Finance tweeted at 10pm on the 26th, stating: "The funds that were hacked have been returned to Defrost Finance. Affected users will soon be able to retrieve their assets."
At this point, the hacker incident has come to a happy conclusion in just 2 days. However, this has sounded the alarm for security companies and the ecosystem.
Hoi reviewed on Twitter why he chose this mine and listed several reasons: 1. The contract has been reviewed by myself and employees, and third-party hackers cannot hack it. 2. Audits by Certik and others. 3. This project has been promoted on many Avax platforms, even recommended by official accounts. 4. Later, when I came up with the idea, I found that the returns of other Defi mines were average, and everyone in the community was easy to talk to.
An auditing firm surprisingly has no basic understanding of the team behind the audited project. Only securing the contract does not prevent subjective malice, so it is essential to have KYC of the team. Therefore, some users have questioned CertiK. If the team refuses KYC, you should refuse to provide an audit. In addition, the Chinese official of Avalanche public chain has promoted the project multiple times, so the ecological side needs to be cautious in promoting the project.
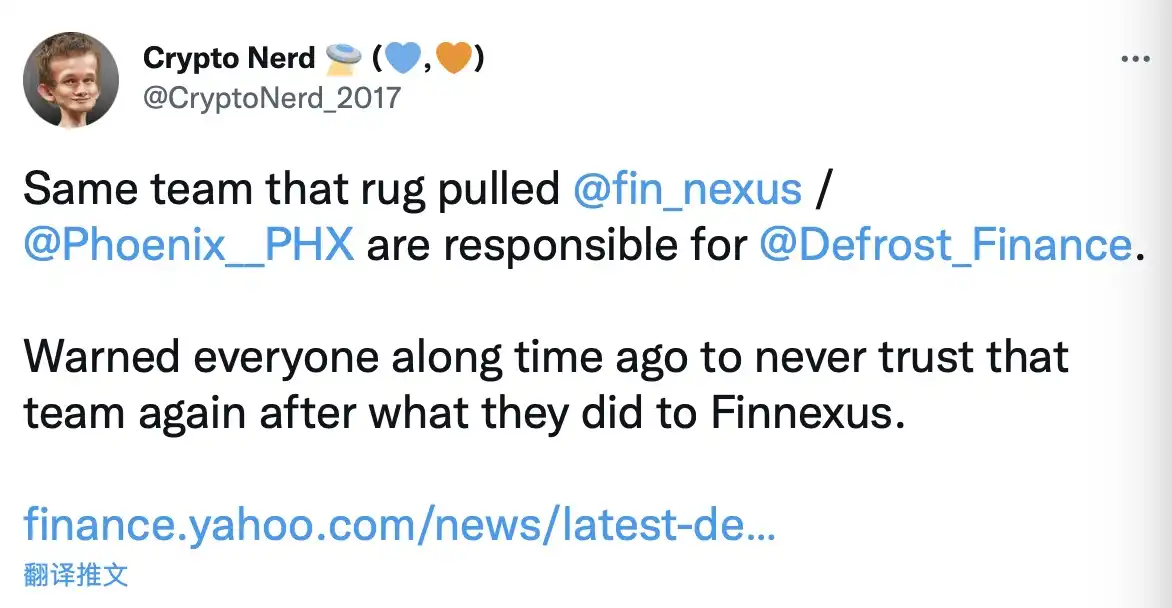
In addition, some users have claimed that the project team behind DefrostFinance is the same team behind the previously hacked projects Finnexus and PhoenixFinance. The authenticity of this information is still to be verified, but it serves as a reminder to users to choose projects with real-name founders, as anonymous founders may have ulterior motives.
Original article link
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia

 Related Articles