Panoramic Tracking of Fake Wallets: In-depth Demystification of the Fake Wallet Phishing Industry Chain
Original title: "Protect Your Wallet! Panoramic Tracking of Fake Wallets"
Original Source: SlowMist Security Team
Foreword
Small A Recently received a text message about a trading platform event, so Little A entered "xx Wallet Official" in the browser and clicked on the top link , download the App-create a wallet-transfer assets, all in one go. After a while, Little A received a notification that the transfer was successful, and the balance in his wallet App - ERC20-USDT worth 10 million US dollars - was reduced to zero. Little A later realized that the app was fake and downloaded the phishing app by himself.
Slow Mist published on November 24 last year about fake Analysis Report on Black Wallets—Slow Mist: Fake Wallet Apps have caused tens of thousands of people to be stolen, with losses as high as 1.3 billion U.S. dollars. It is conceivable that as time goes by, how much the stolen losses will be until today surprise.
Analysis
Today we analyze from the big data side how many fake wallets there are.
1, MetaMask It is currently the world's largest browser plug-in wallet. In April 2021, ConsenSys, the parent company of MetaMask, stated that the number of monthly active users of the MetaMask wallet exceeded 5 million, a five-fold increase in six months. 4 times, the number of users exceeds 80 million.
MetaMask is so massive The number of users is naturally the first goal of black production, let's take a look at how many counterfeit MetaMask there are:
< /p>
First, search through a professional browser:
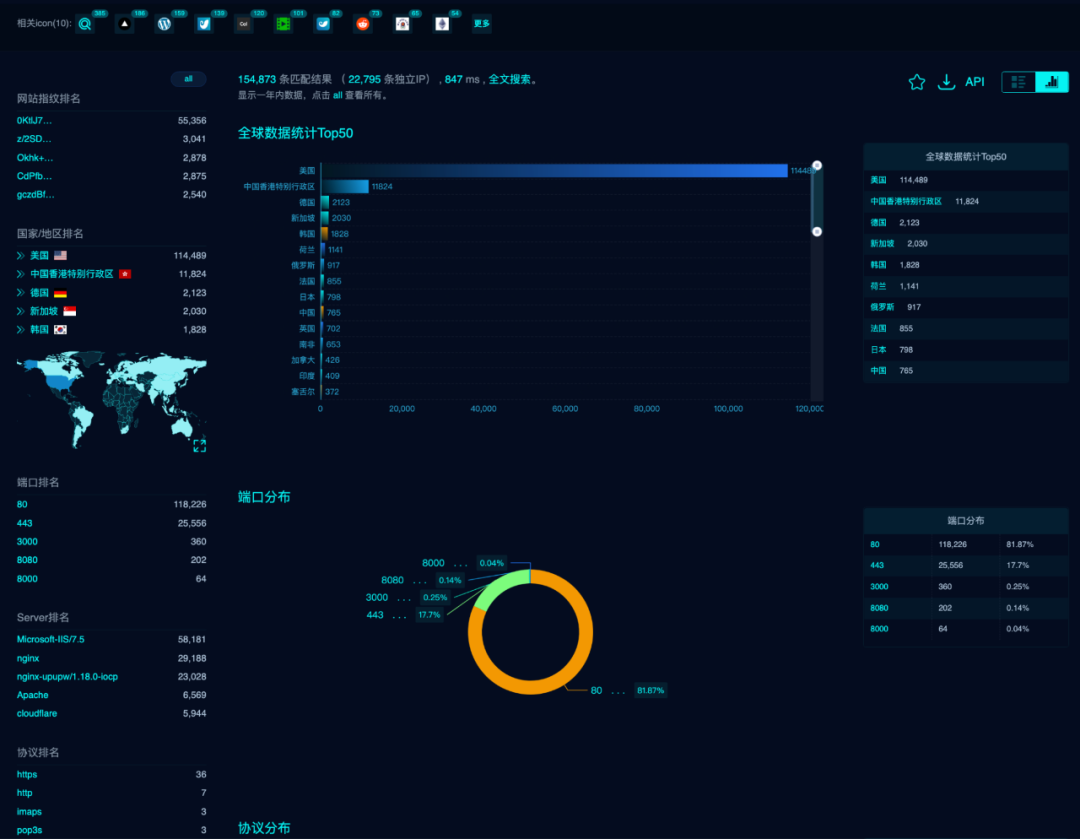
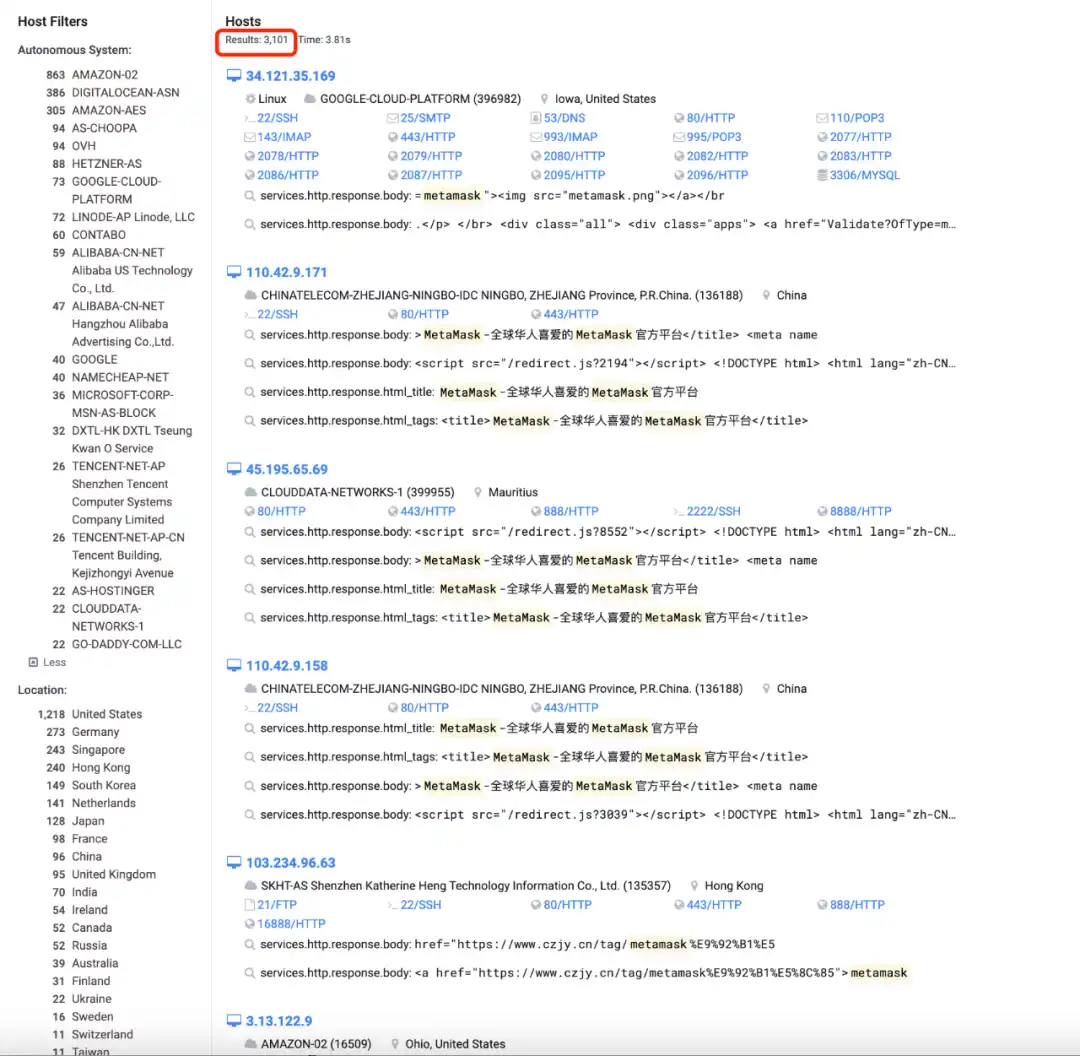
The search results show that there are 20,000 + relevant results, of which 98% of the IP/domain names are false Scam link.
Further tracking, such as finding MetaMask Download:

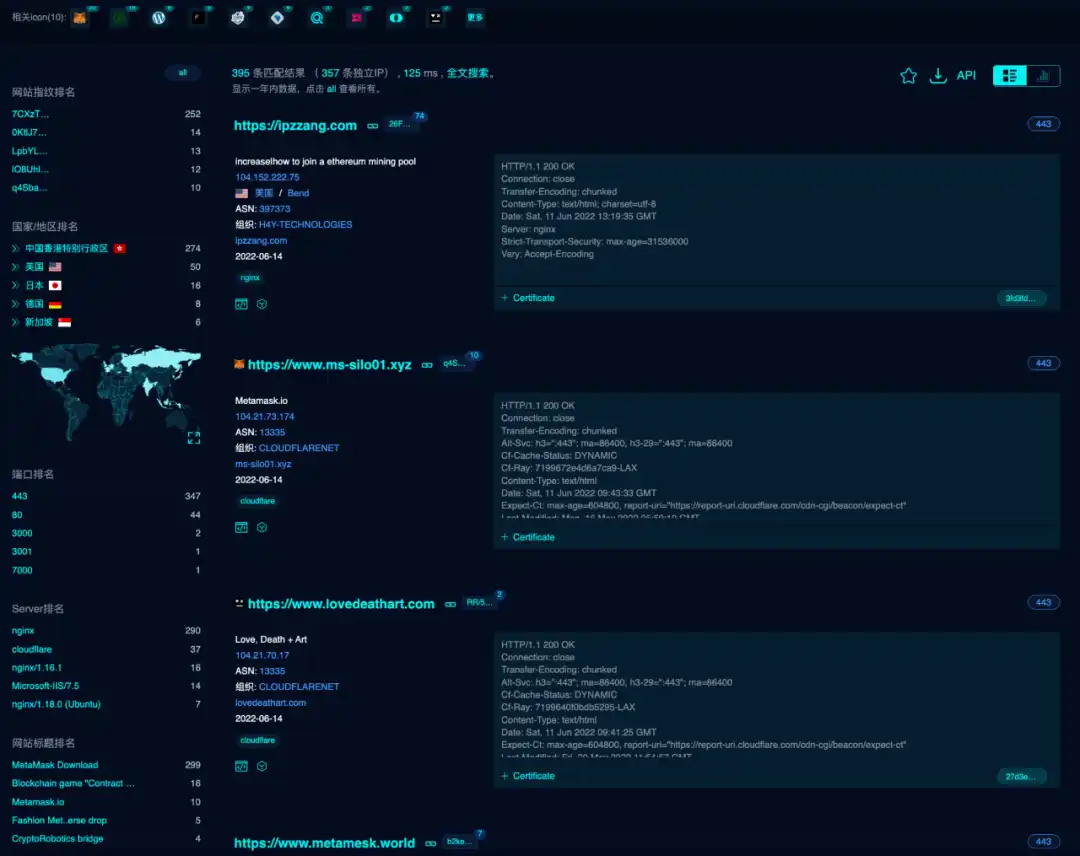

At a glance, they are all phishing websites, and anyone familiar with security should know that ports such as 888/HTTP and 8888/HTTP And service is the default configuration of the pagoda system, and the simple and easy-to-deploy attributes of the pagoda lead to a large number of black and gray products. The above related IP/domain names are all false and fraudulent links to induce users to visit and download.
Let's go one step further Interesting to watch.
Search first: MetaMask Authorization management (the management background of Heihui production phishing)
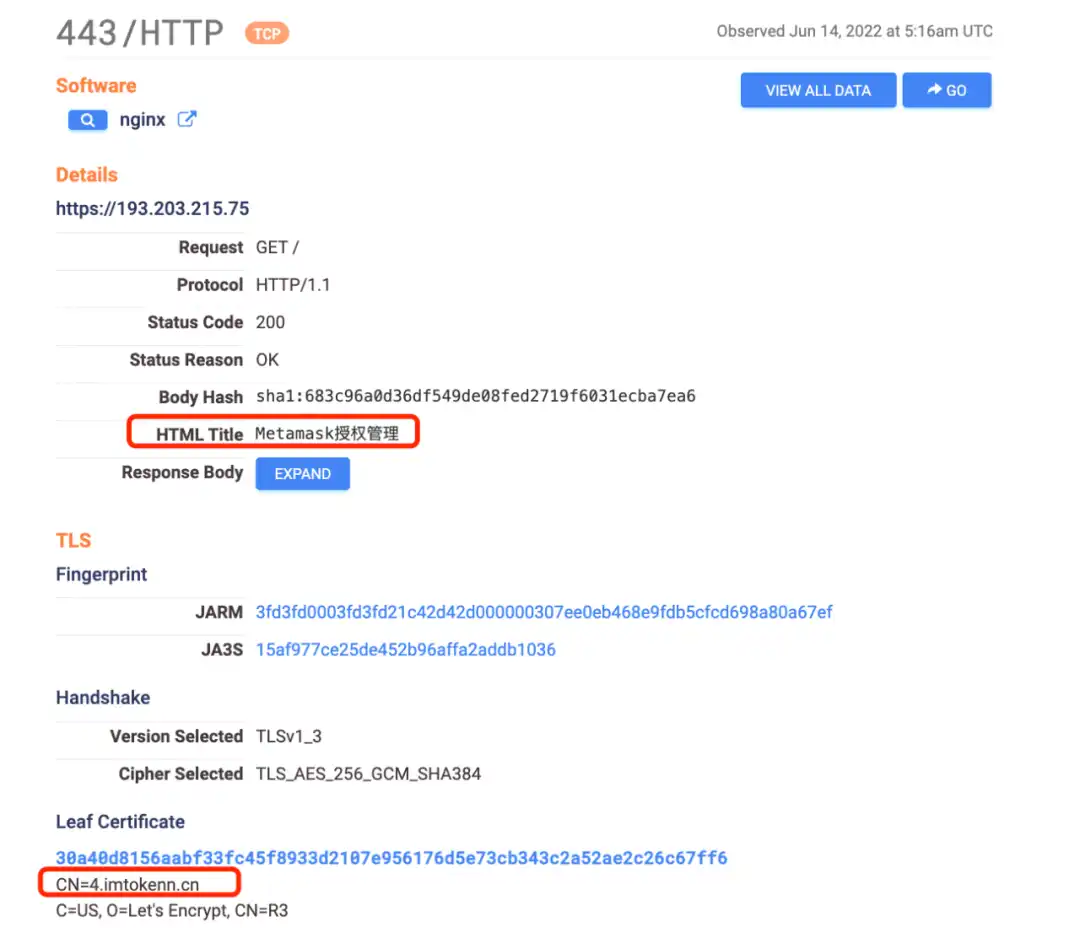

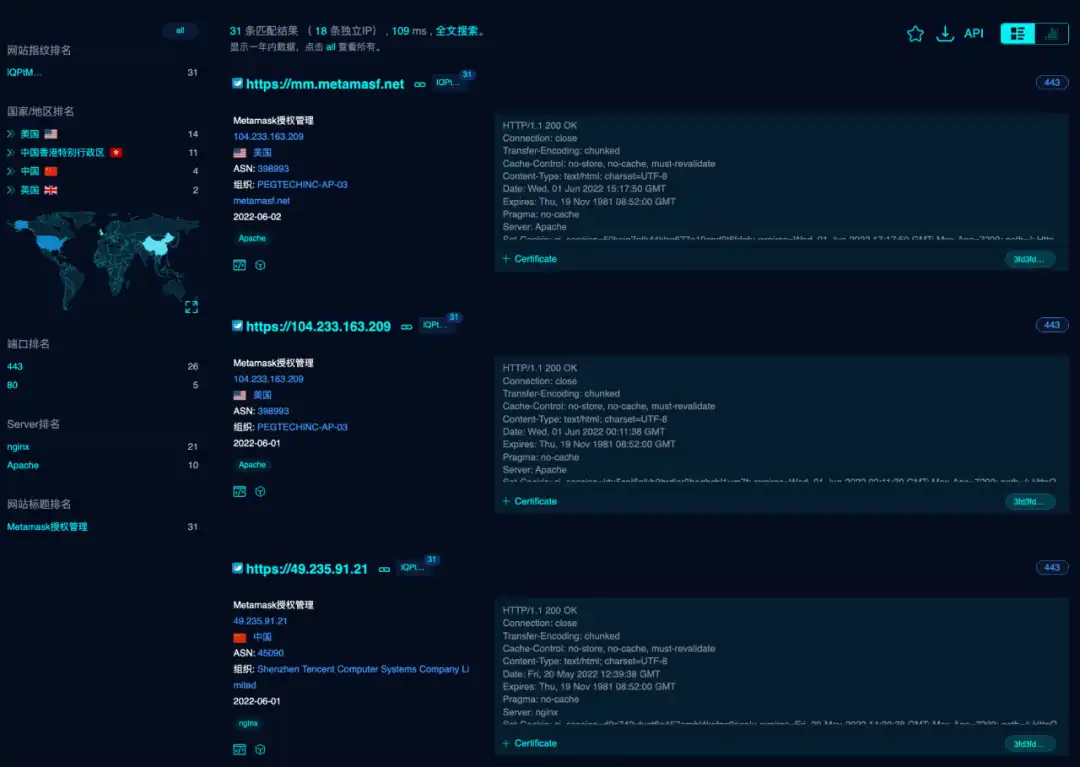

These are all domain names related to the background management of the black industry. We also shuttled the domain names together. Some of the captured domain names and related resolution times are displayed as follows:
< br>

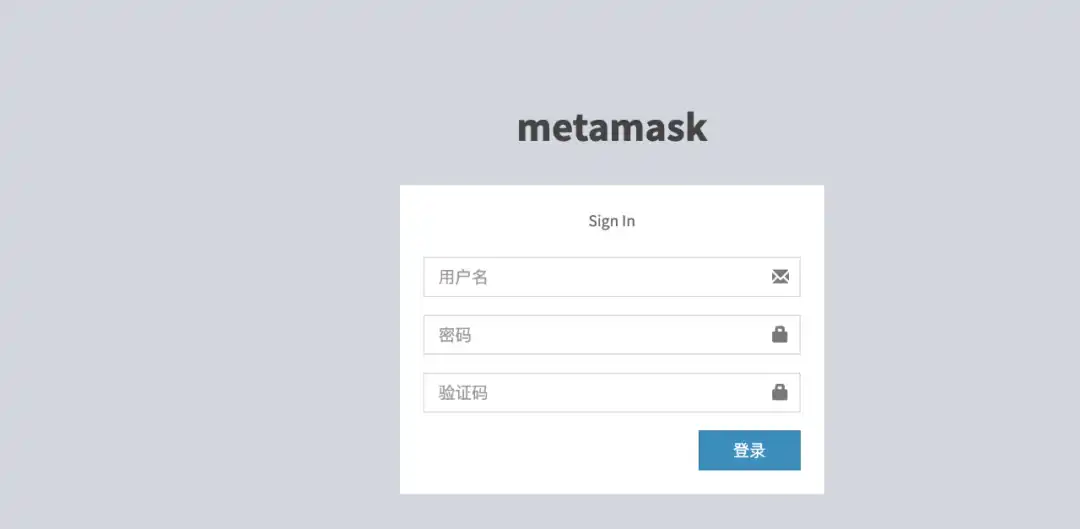
Vue+PHP environment, the deployment method is as follows:
< br>

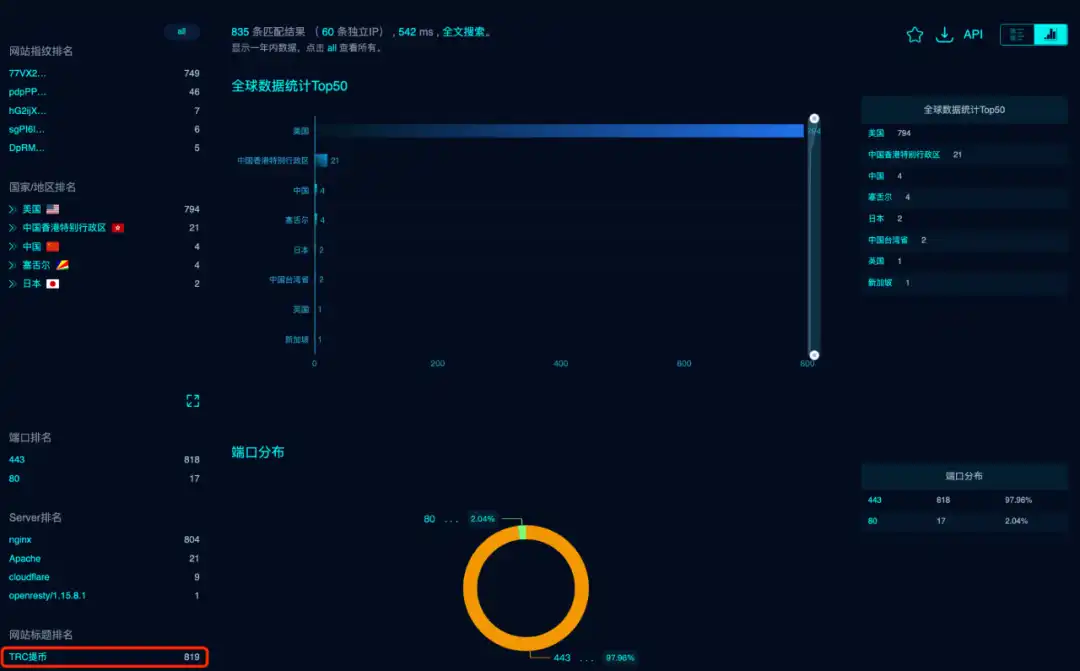
2, imToken authorization management is the same way:
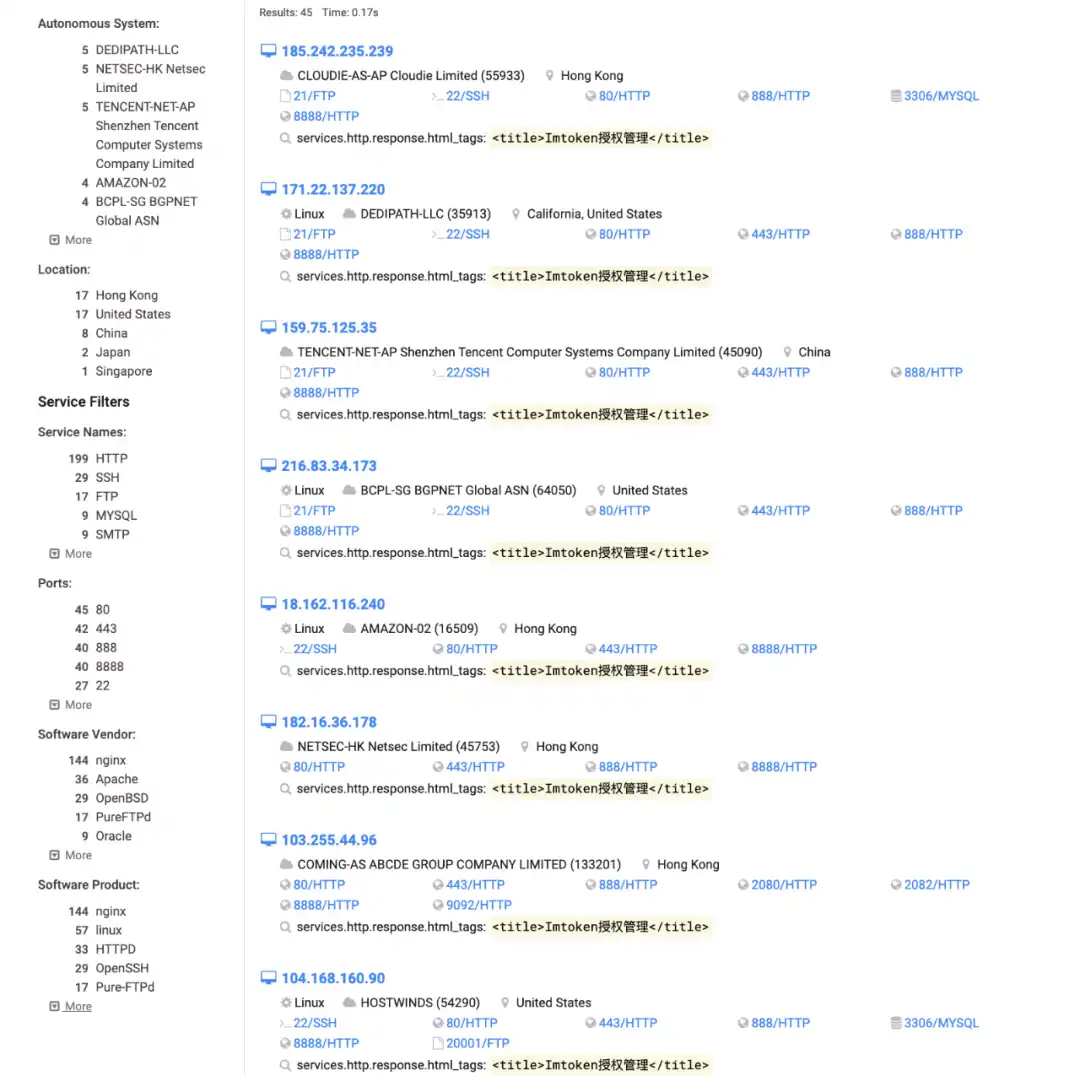

TokenPocket Authorization Management:

Fishing background:
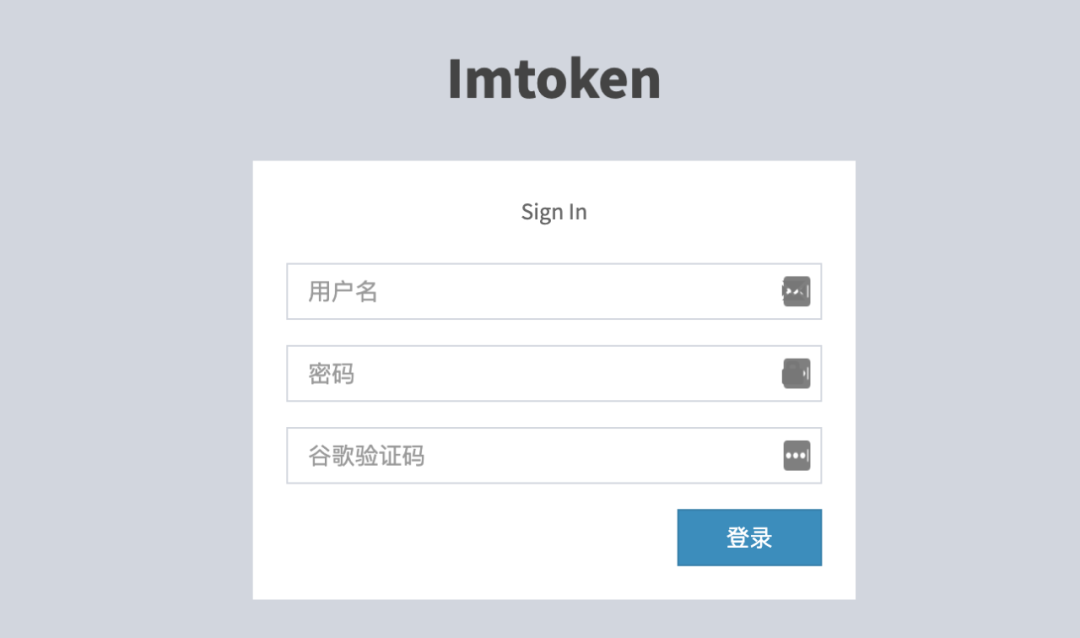
Background related service industry chain:

< /p>
3. After obtaining relevant victim information in the background, the attacker operates through the withdrawal API interface:
< p>
Let's take a look at the code:
< br>

Involves JS, configuration JS, and transfer JS of basic web services.
Look at this again: var _0xodo='jsjiami.com.v6', I have to say , The black and gray production has surpassed most regular Web sites, and they are already implementing JS full encryption technology.

< /p>
Configuration:
< img _width="578px" src="https://image.blockbeats.cn/upload/2022-06-24/72417ebecbb73996b7eb30ded88ebc4200ae844b.png?x-oss-process=image/quality,q_50/format,webp" alt=" Image">

< br>
Here sc0vu/web3.php: "dev-master" is a php interface system for interacting with Ethereum and blockchain ecosystem.
After analysis, it is found that after the attacker obtains the private key and other relevant information, he transfers the relevant stolen assets through api.html calls. I won't repeat them here.
Do you think this is the end?
You think their goal is just to counterfeit MetaMask, imToken, TokenPocket and other wallets website?
Actually, besides forging these well-known wallets on the market In addition, they also imitated and built related trading platforms for phishing, let's take a look:
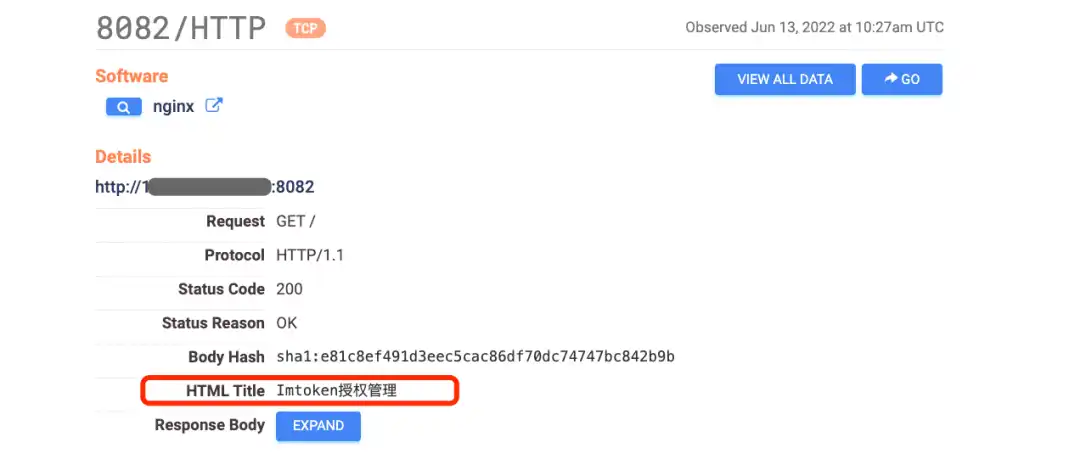
For example, under this IP, we found other information besides phishing pages and background:


Fake trading platform phishing site , and more than one:
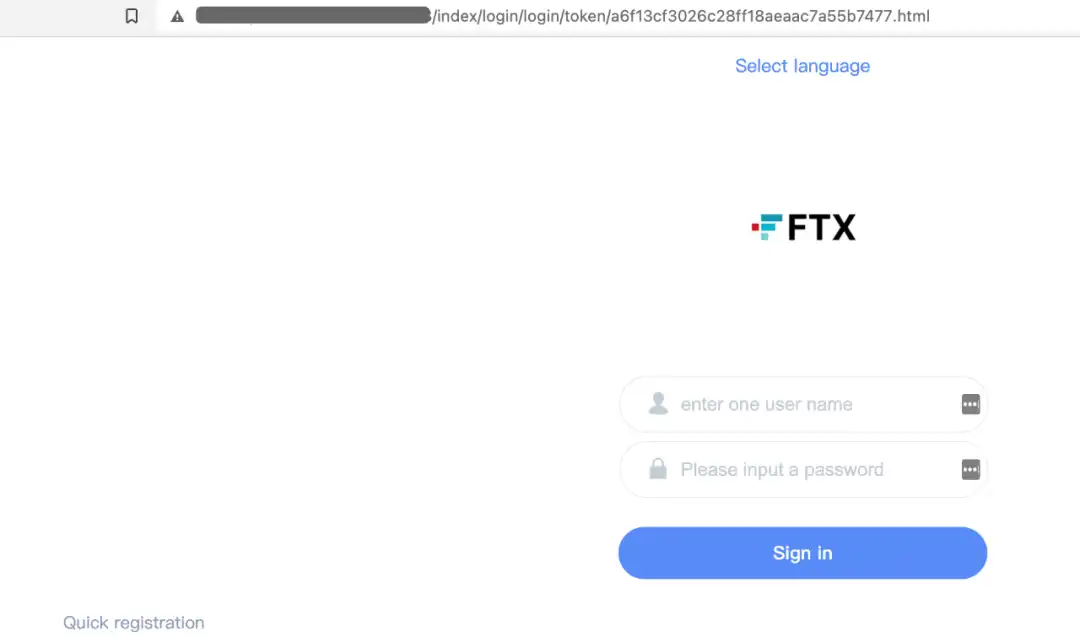
A cryptocurrency phishing platform built using the Laravel framework:
< /p>

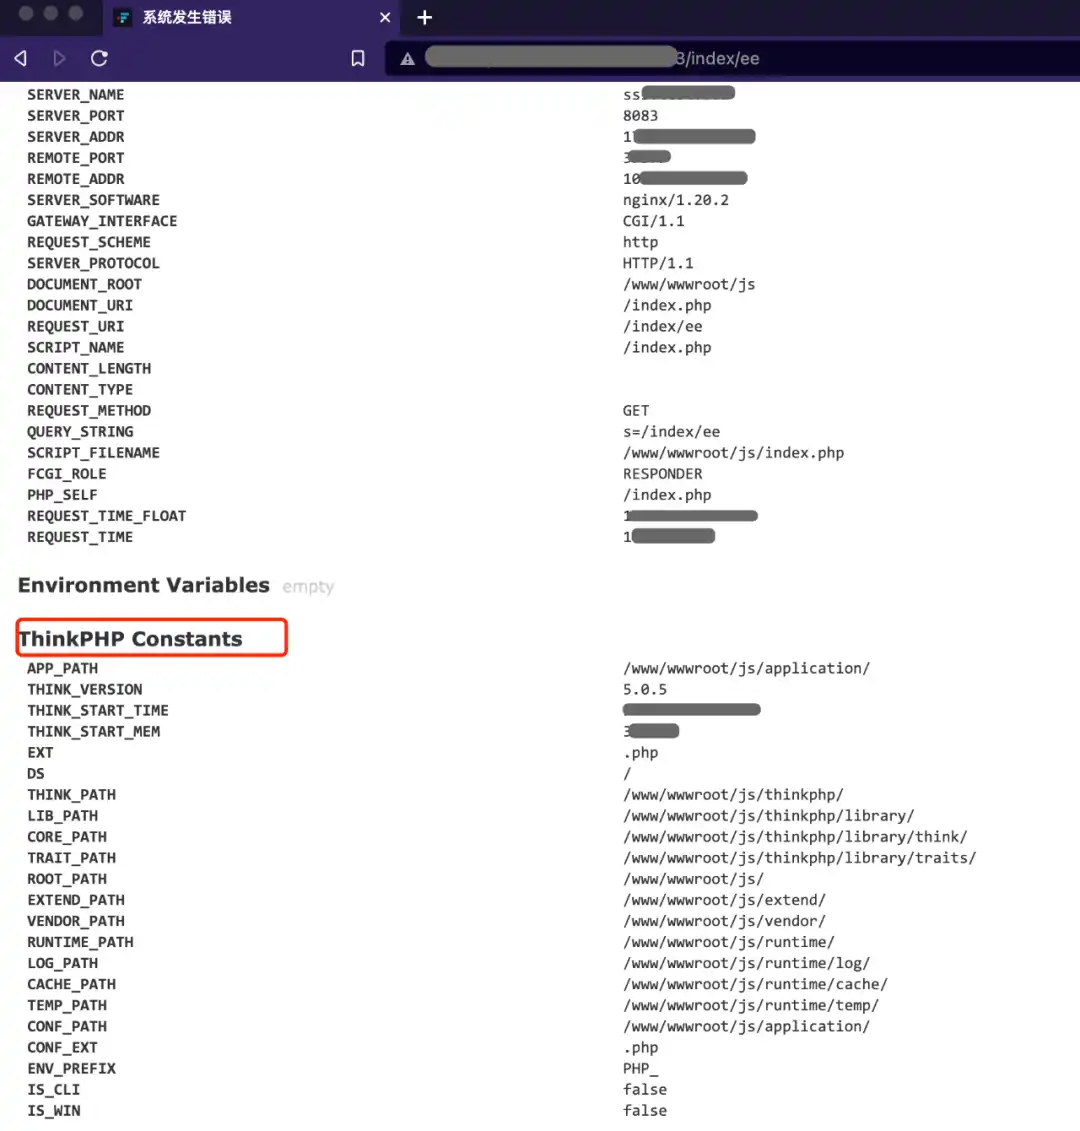
A phishing site imitating FTX platform built using the ThinkPHP framework:
Let’s take a look at the SaaS version of the phishing scam template sold directly online:
< p>
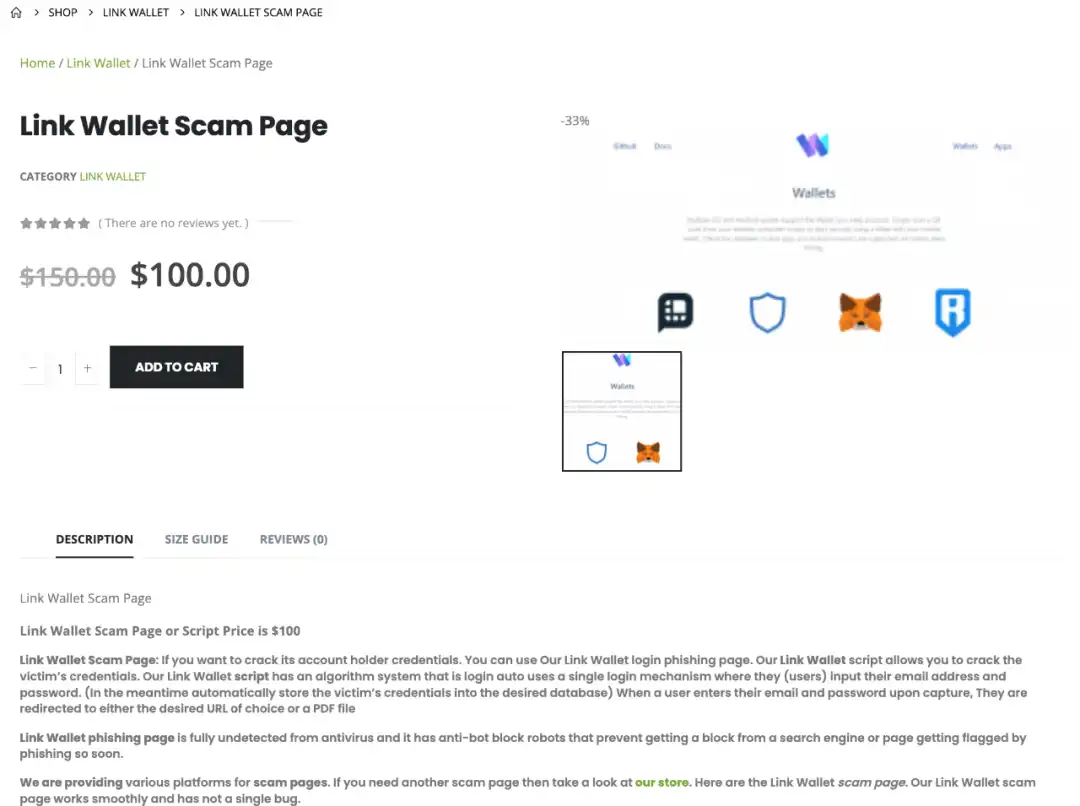
Cheater platforms support most mainstream wallets (the wallets here are also their fake)

The phishing and fraud industry chain for cryptocurrency and NFT is very complete, professional SaaS service, rapid deployment, Live now.
Further investigation Discover the relevant background management system, as shown in the following figure is the cloud desktop management background, which is used to control the relevant information of the trading platform:
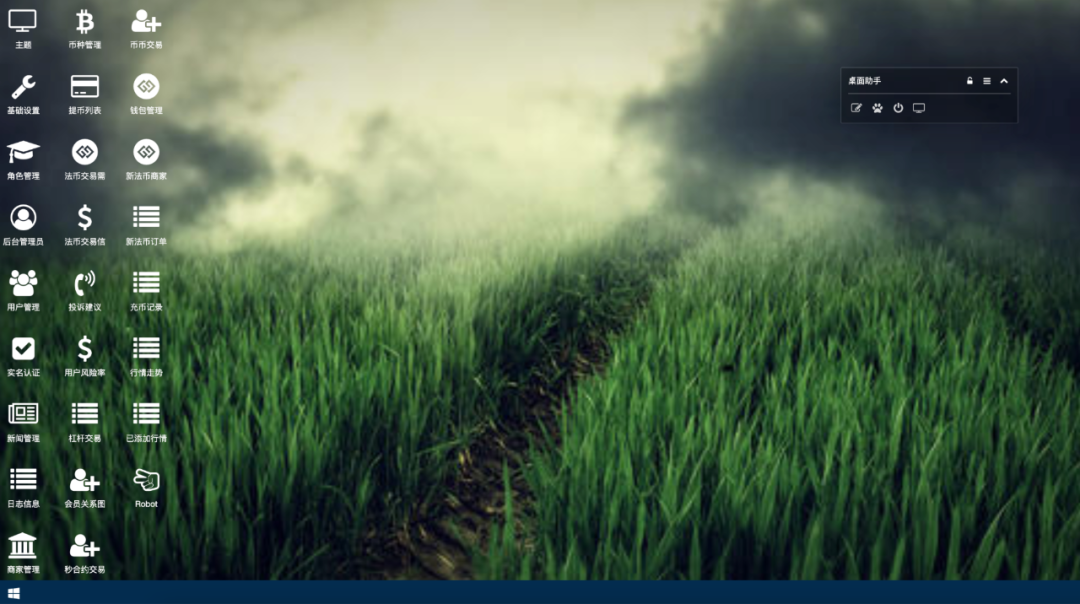
The classification is clear and the functions are complete, and the advanced and professional degree of black and gray production has far exceeded imagination.
Summary< /h3>
This article mainly analyzes the panorama of fraudulent wallets from the perspective of technical means. Very low, and a process-oriented and professional industrial chain has been formed. These scammers usually use some tools to copy well-known wallet project websites, tricking users into entering private key mnemonics or inducing users to authorize. We recommend that you always verify the URL of the website you are using before attempting to download or enter it. At the same time, do not click on unknown links, and try to download through official webpages or official media platforms to avoid being phished.
Original link
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia
 Related Articles