



2025 Guardianship: $500M and 70M Intercept | OKX Chronicle
Source: OKX
In the past, people were accustomed to the "hackers breach a major project, news spreads for a few days" type of single-point explosion. However, this year, risks have gradually permeated every seemingly ordinary on-chain operation: For example, the convenience brought by on-chain protocol upgrades has also become a new phishing entry point; Fake websites disguised to the pixel level; Malicious apps on mobile phones silently listening to the clipboard in the background; Phishing links after social media hijacking are even more "official" than the official ones; and those aging old contracts that were once authorized may also be awakened by hackers one night.
A Chainalysis report pointed out that as of mid-2025, the amount stolen from crypto platform services, including exchanges, wallets, and custody services, has exceeded $2.17 billion, and if the trend of disclosed incidents continues, it may continue to rise throughout the year. The core issue in 2025 is no longer "whether there is risk," but in the risk environment, how an ordinary user can obtain real security protection?
More and more data and events have repeatedly proven that only by intercepting risks in advance and combining them with user-friendly, low-threshold self-service tools (such as bulk deauthorization, device scanning), can personal losses be truly reduced. It also makes users truly feel that "security is in their own hands." This is also the moment in 2025 when OKX brings "security sense" to users. In the past year (2025.01–2025.11), OKX Wallet helped users recover a total amount of over $500 million in losses, with an average response time of only 3 seconds for tracking blacklisted addresses, and a total of over 70 million risk information flagged and intercepted.
Image: OKX Wallet Full-Stack Security Protection
I. The "Deformed" Security Risk
According to CertiK's report, the total crypto asset losses in the first half of 2025, including wallet theft, phishing, fraud, server-side attacks, etc., amounted to approximately $24.7–25 billion.
From 2024 to 2025, the industry's security posture exhibited two parallel trends: a few large exchanges or servers being breached, resulting in high losses; at the same time, individuals also experienced phishing, malware, and social engineering scams, leading to frequent small losses. The coexistence of high-value centralized losses (platform) and high-frequency small losses (users) puts double pressure on the overall industry security.
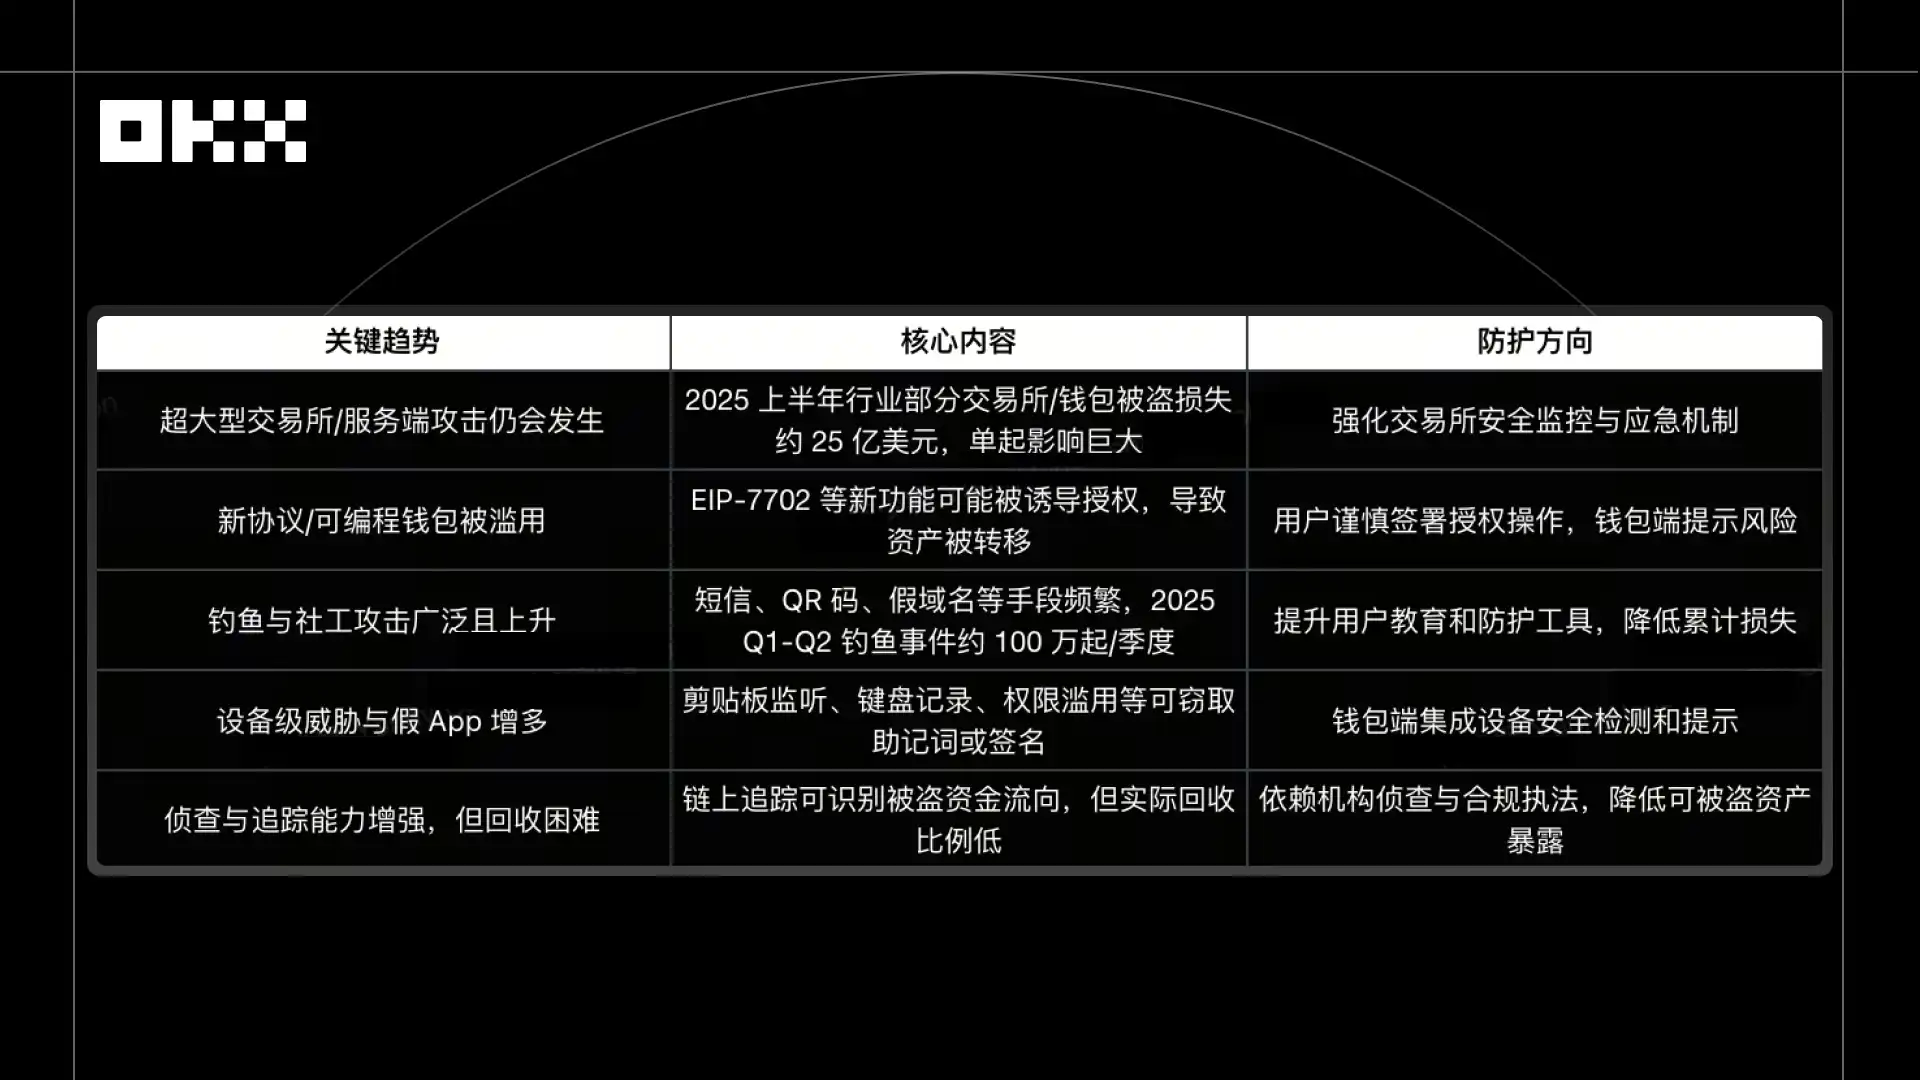
Phishing and social engineering attacks remained high in the first half of 2025. APWG data shows that there were over 2.13 million attack events in Q1-Q2, a 13% increase from Q1 to Q2. Particularly, a broad spectrum of security incidents is not due to users being "too clueless," but rather because risks have "morphed" into something that ordinary people find hard to distinguish:
A seemingly normal address could be a highly similar fake address, leading to fund misdirection upon copying.
A familiar official website link could be a hijacked or disguised phishing mirror, challenging to discern.
A seemingly secure on-chain operation could conceal a malicious upgrade request, leading to fund theft through multi-signature or authorization operations.
An apparently harmless plugin could be silently recording mnemonic phrases or signature operations in the background.
A commonly used wallet or contract could also be abused in authorization or upgrade processes, with concealed risks where users could lose assets without triggering any vulnerabilities.
Security events in 2025 indicate that hacker attacks have shifted from direct exploitation of code vulnerabilities to exploiting user psychology and habits. Annual reports from several security firms, including CertiK, Chainalysis, Ledger, and Kroll, show that these attacks account for over 70% of total losses. While the individual amounts may not be significant, they are nearly impossible to defend against because users often fall victim even when they "haven't done anything wrong." Unlike past major project collapses that were more apparent, these "morphed" risks are covert, widespread, easy to trigger, do not rely on vulnerabilities, and only require one-time authorization, signature, or click to cause losses. Even experienced users can fall prey. Therefore, relying solely on smart contract audits or on-chain monitoring is no longer sufficient. Protection also needs to integrate wallet security, contract whitelisting, reputation systems, and visual anti-phishing mechanisms.
II. The "Peace of Mind" Moment Brought by OKX
Moment 01: The "Mole" in the Phone Gets Caught
In 2025, an NFT collector downloaded a "purchase assistant (pseudonym)" app on an Android phone to participate in the hot NFT project's purchase. After downloading, he noticed abnormal wallet operations, but initial checks did not reveal any unauthorized transactions. On the surface, this app appeared to be a normal auxiliary tool, but it actually possessed high-risk behaviors such as stealing clipboard content, monitoring keyboard input, and abusing accessibility permissions. Once activated, it could lead to the theft of mnemonic phrases and private keys, thereby compromising user asset security.
After enabling OKX Wallet's "Device Security Scan" feature, the system performed real-time active scans on the Android device, accurately identifying the plugin's attempts to monitor clipboard and keyboard input. OKX's device-level protection covers Windows systems, browser plugins, and mobile devices, detecting potential local malicious software and assessing their threat levels to mnemonic phrases, private keys, and transaction security. The scan report indicated high-risk behavior by the plugin, and the system promptly alerted the user of the risk. Following the prompt, the user immediately uninstalled the plugin, eliminating the potential threat.

Moment 02: Clicked on Phishing Website? Intercepted in Advance
In 2025, a user was getting ready to participate in a project's token sale event. When entering the project's page through a social platform, the user did not notice that the project's official account had been hijacked and had posted a phishing link to a spoofed staking platform. Upon clicking on the link, before the page could fully load, the OKX Wallet proactively displayed a red alert box, indicating that the website had been flagged as a high-risk phishing site, advising the user not to connect the wallet or perform any signing operations.
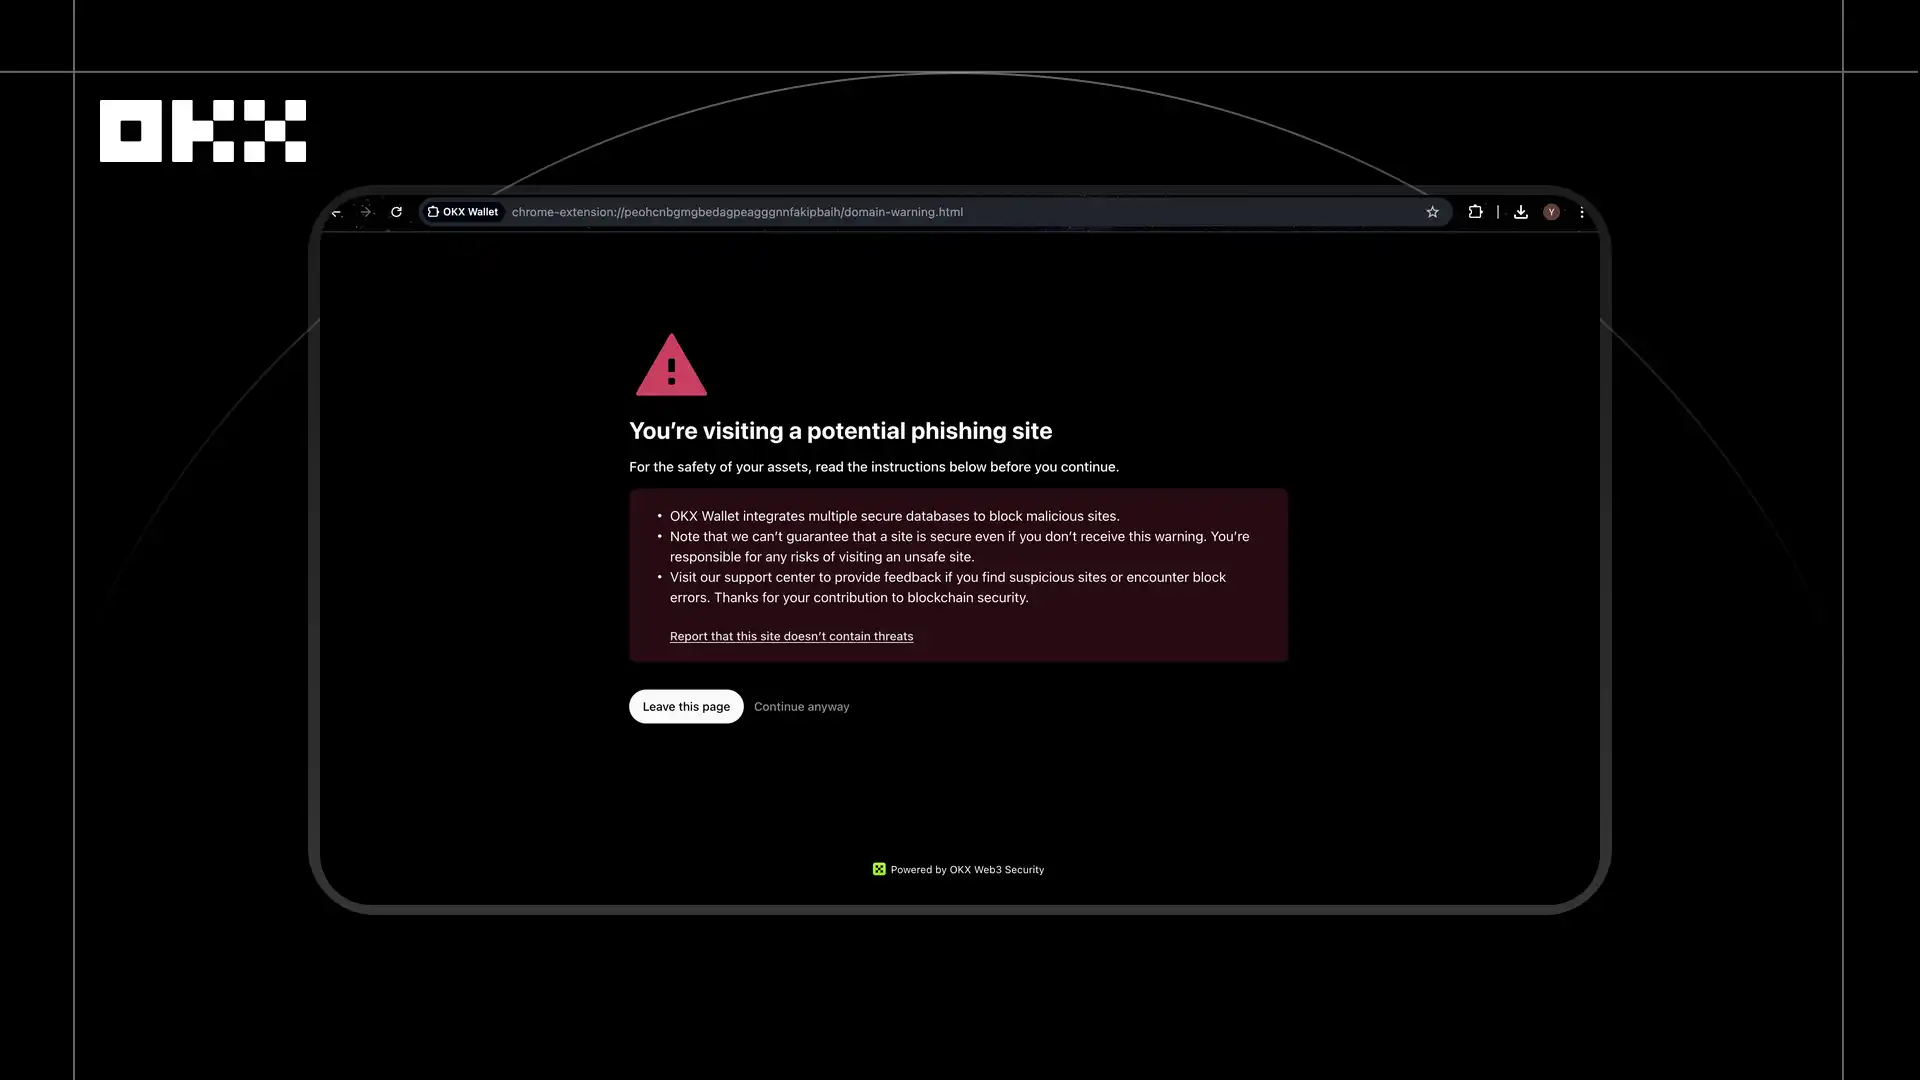
This interception is based on OKX's malicious DApp and URL detection system. The system conducts static and dynamic security scans on links and DApp pages before user access, identifying page spoofing characteristics, malicious redirection behavior, high-risk contract calls, and abnormal script activities. It relies on a real-time updated URL risk database to make a classification judgment. When a phishing website or fraudulent content is detected, the system immediately blocks access before any interaction occurs between the user and the page, preventing asset theft due to erroneous authorization.
Moment 03: One-Click Revoke of Risky Authorizations
In 2025, a user who had been actively participating in various on-chain projects discovered, while reviewing their history, that a project contract they had used in the past was exposed to the risk of authorization misuse. Having been engaging in airdrops, DeFi, and NFT projects for many years, the user had accumulated a large number of idle authorizations that needed to be cleaned up promptly to avoid potential asset misuse. For example, a protocol you have authorized could cease operations at any time, taking away the funds you authorized, or it could fall victim to a hack, also resulting in a loss of your funds. Therefore, revoking idle authorizations is essential. However, revoking authorizations one by one is not only time-consuming but also incurs high gas fees, making the process highly inefficient.
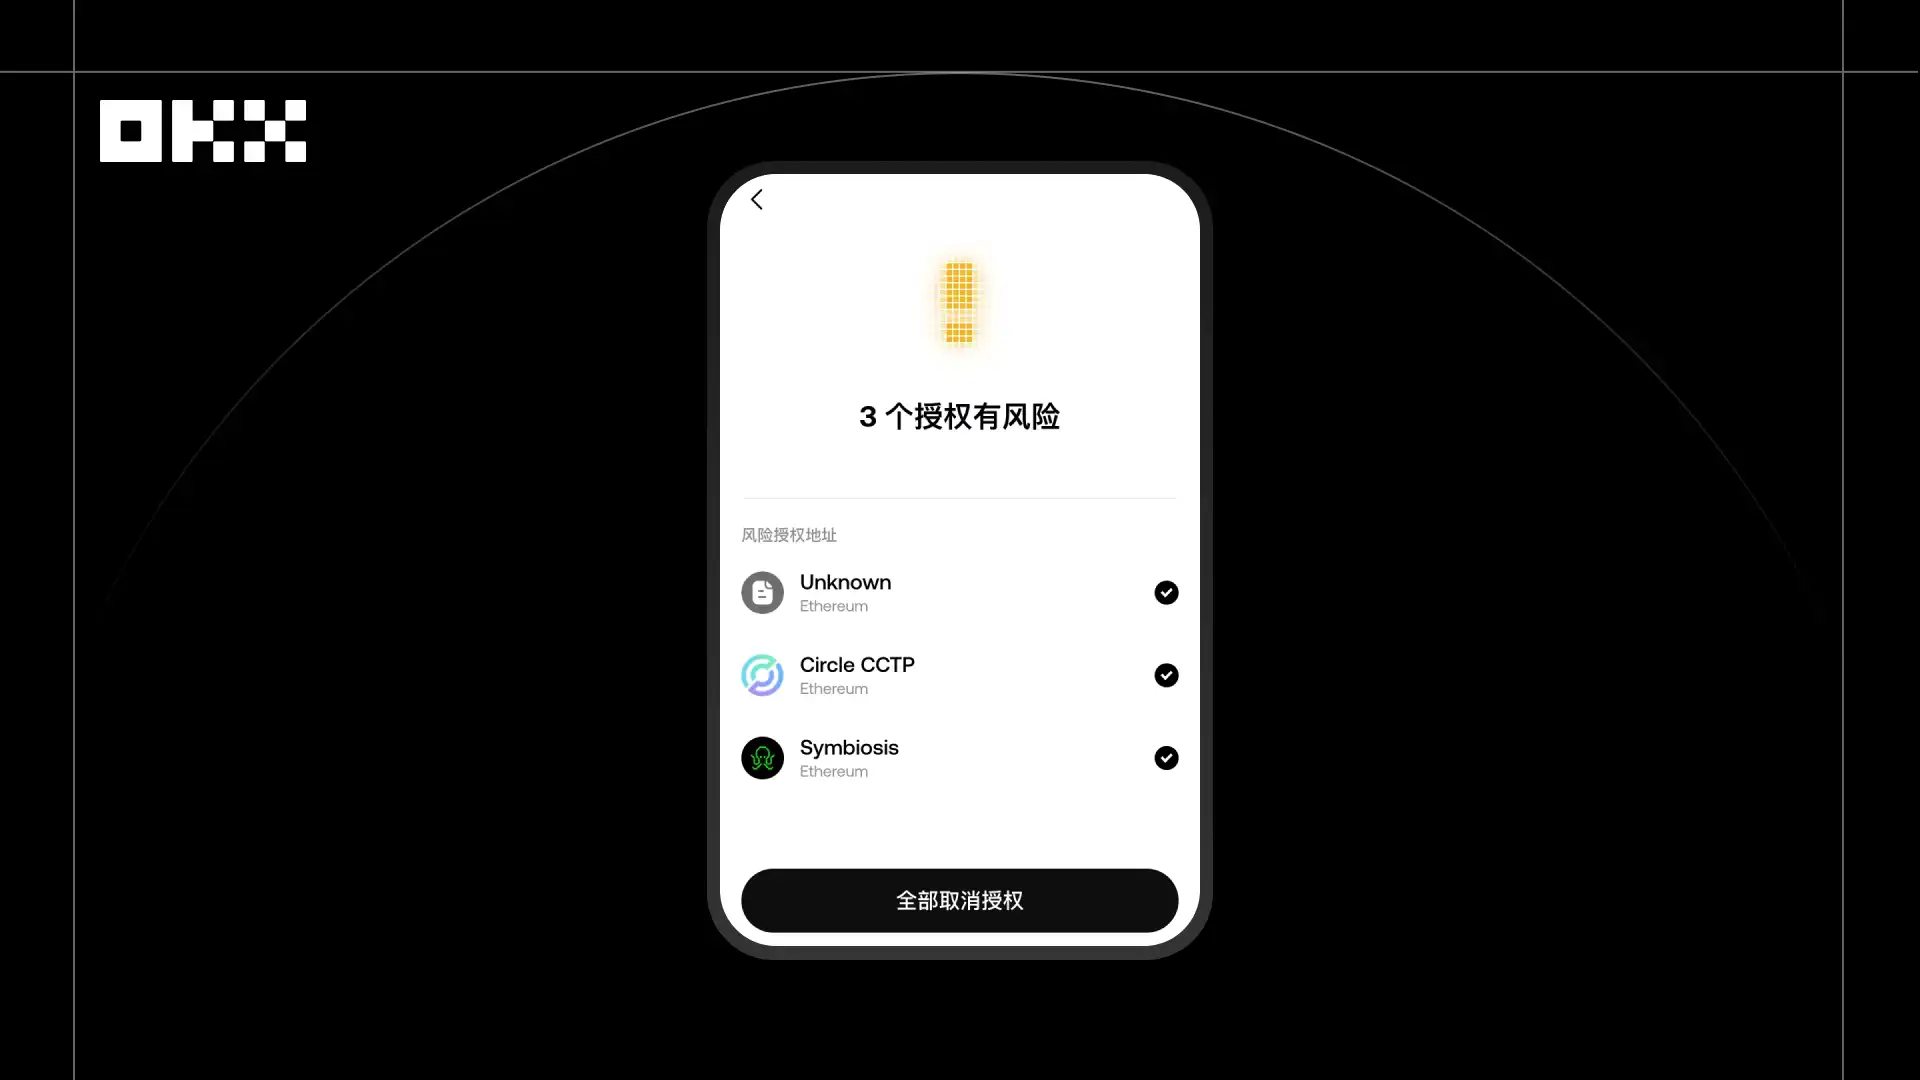
After using the OKX Wallet's authorization management tool, the system automatically scanned their historical authorization list and provided batch revoke capability. By selecting multiple risky authorizations, a user could complete all revokes with just one on-chain transaction. For users whose wallets had been upgraded to support the EIP-7702 delegation contract, this feature allowed the free revocation of all authorizations without the need for individual processing. Compared to the traditional single revoke method, batch revoke not only significantly enhances processing efficiency but also, on average, reduces gas costs by over 30%.
Moment 04: Before Paying Gas Fee, Wallet Says "Stop"
Fishing Attack Intercepted by EIP-7702. In 2025, during the launch of EIP-7702, a user came across someone generously sharing a mnemonic phrase on a social platform. Out of curiosity, the user imported it into an EVM address wallet and attempted to send a small amount of gas fee to that address to withdraw USDT assets from it. At first glance, the address seemed to be a regular EVM wallet, and the user believed it to be safe. However, in reality, the address was leveraging the EIP-7702 standard to masquerade as a regular receiving address, with the delegation contract deployer having advanced permissions. Once the user sent the gas fee, the funds could be immediately transferred out.
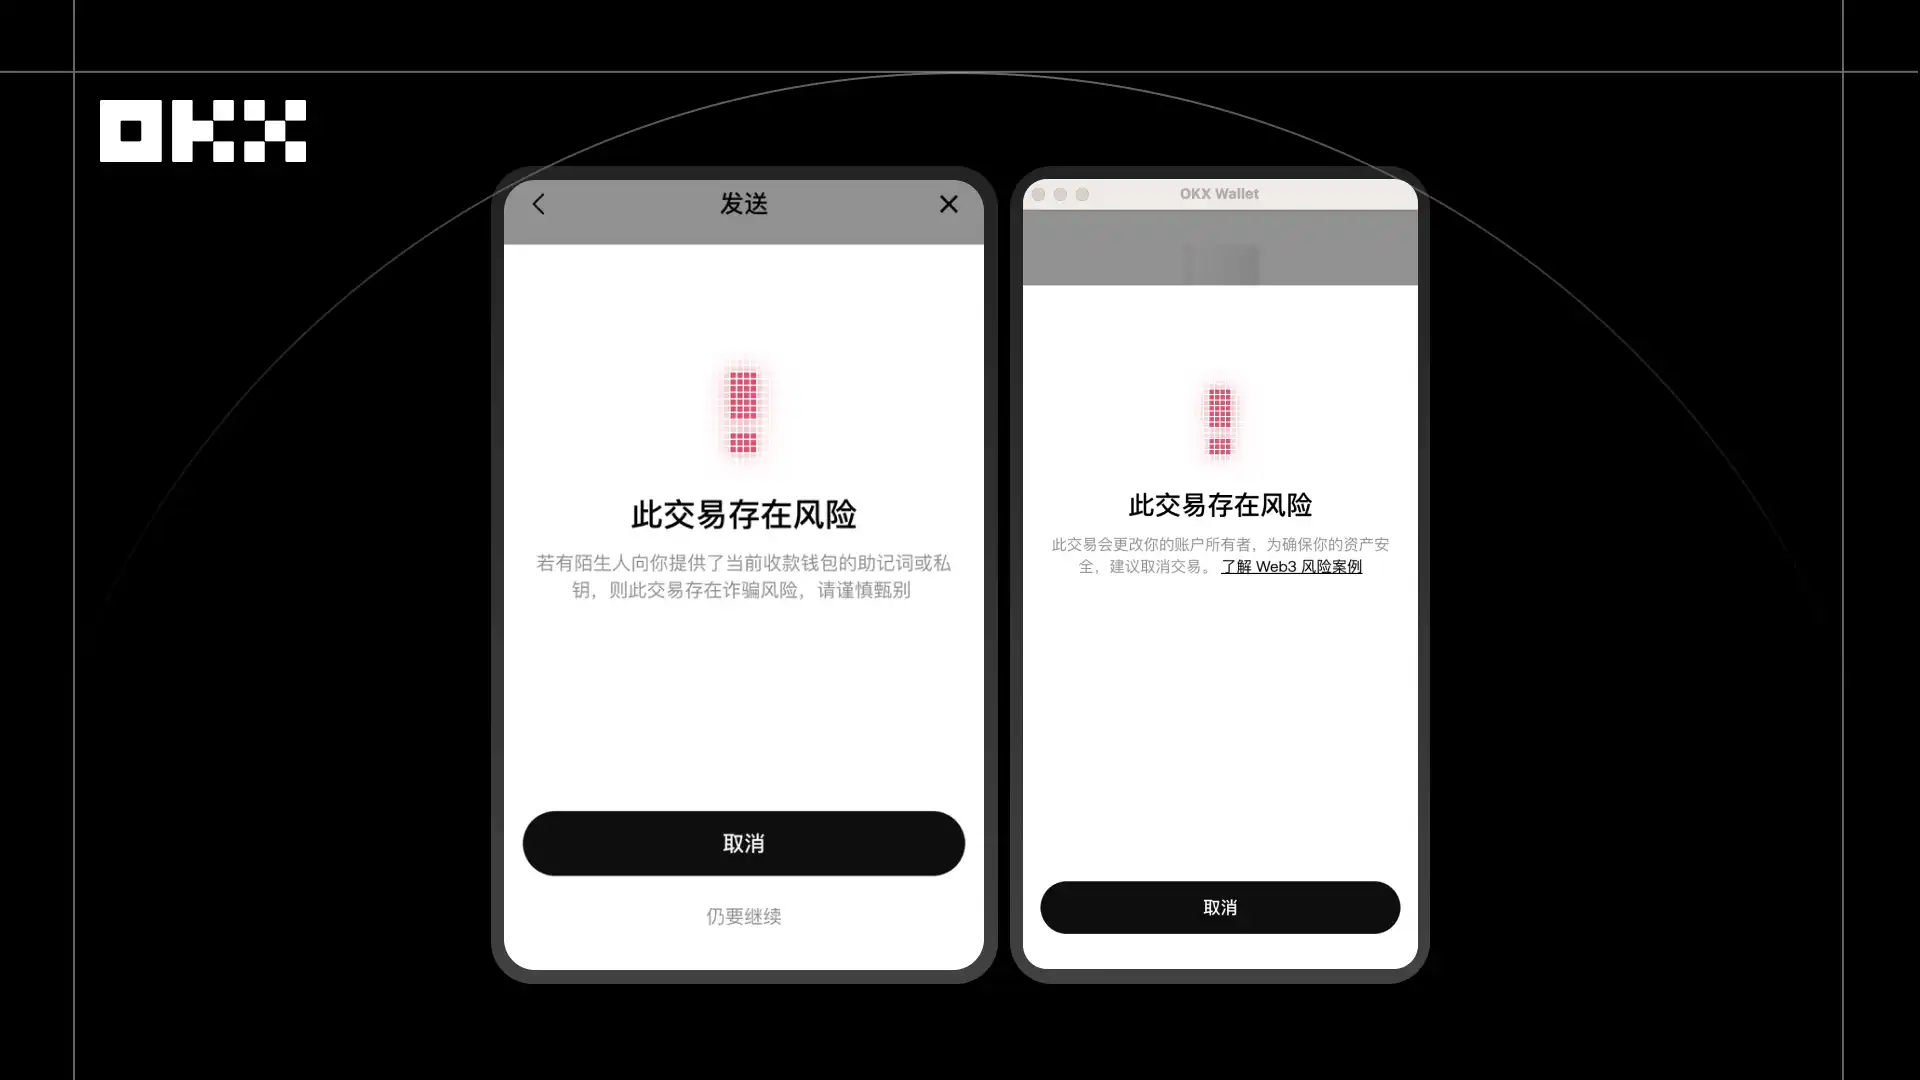
When a user attempts to make a transfer, the OKX wallet's real-time risk control system immediately identifies the transaction as high risk and triggers an interception. Through on-chain behavior analysis, transaction history, and smart contract logic detection, the system accurately identifies potential risks, including contract-disguised ordinary addresses, EIP-7702 phishing attacks inducing user authorization or gas fee payment, and abnormal contract interaction behavior inconsistent with user operating habits. Additionally, with the rise of Move series public chains like Aptos, to address Move Virtual Machine attacks that steal funds by tampering with the public-private key mapping relationship, the OKX wallet can analyze MoveVM interaction behavior in real time. Upon detecting key tampering risks, it actively interrupts the transaction to prevent asset theft. The transaction is blocked during the confirmation stage, and the interface clearly alerts the user, "The receiving address is a high-risk address, and your transfer funds may be diverted," effectively preventing fund loss. After the event, users not only avoid financial losses but also enhance their awareness of cutting-edge on-chain threats through understanding the attack principles and risk patterns highlighted in the alert.
Time 05: Address Tampered, Withdrawal Frozen!
In addition to the OKX wallet, this sense of "security" is also reflected in the OKX exchange.
In 2025, a user received an on-chain payment address from a friend in a social app without realizing that a malicious program lurking on their phone had quietly tampered with the message content. The address the friend should have sent was originally ABC123**456DEF, but what the user saw had been tampered to ABC234**567DEF. When the user attempted to transfer to this incorrect address, the OKX system promptly detected the anomaly. With OKX's persistent reminders, the user was guided to identify the address anomaly, helping them avoid loss and increasing their awareness of on-chain scam methods.
To counteract this highly covert tampering attack, OKX introduced a dedicated address tampering protection strategy on the platform. Before a user initiates a withdrawal, the system performs real-time detection of the receiving address using on-chain behavior analysis and risk models to accurately identify address tampering risks. Once an anomaly is detected, the platform temporarily restricts the withdrawal, guides users through a risk mitigation process to identify the risk source and troubleshooting methods, assists users in verifying and correcting the address, and prevents assets from falling into a hacker's account.
Time 06: Account Compromised? Restrict Transfers and Perform Security Checks
In 2025, a user's account was preemptively identified by the system as "suspected to be part of a fraud chain." The account's fund flows, behavioral characteristics, and device associations exhibited a typical cross-border e-commerce fraud victim pattern before any abnormal transactions occurred. The OKX system promptly implemented protective freezing, and customer service proactively contacted the user to verify the risk.
This type of scam has been rampant in recent years. Scammers use "cross-border e-commerce entrepreneurship" as bait to attract users through advertisements, guide them to register on OKX, claim that "operating a store requires the use of an overseas wallet," and then request verification codes and other key security information under the guise of operating the store on behalf of the user. Once the user completes a deposit, the scammer will immediately take over the account and transfer all the funds out. In response to the characteristics of this type of scam, OKX has established a related risk identification model and deployed automated disposal strategies. When it is identified that a user may be externally controlled, the account's key functions will be immediately restricted, potential transfers will be blocked, and the user will be simultaneously notified to complete risk confirmation and security checks. In this case, the user was included in the protection process on the day of identification. Customer service confirmed that the user was being induced to transfer account custody to the scammer, and the system interception helped the user cut losses in a timely manner before the funds were transferred.
III. Security Services: Evolving from "After-the-Fact Remedy" to "Preemptive Interception"
The blockchain world is like a fast-paced city, where assets, permissions, contracts, DApps, and addresses are constantly in motion, and risks have become smarter, more elusive, lurking in every click, every confirmation, every moment of hesitation. Security is not in the halo of technology or functionality but in those fingertip-touchable moments — in the certainty when an operation is error-free, in the peace of mind when a potential threat is quietly intercepted, and in the tranquility when a complex system quietly safeguards.
Over the past year, the OKX Wallet has continuously strengthened security protection and proactive defense, covering end-to-end monitoring from high-risk domains, spam airdrops to phishing addresses, and blacklisted addresses. Not only has it established a scalable capability in real-time risk monitoring and identification, but it has also advanced a multidimensional, multi-strategy protection mechanism to proactively intercept potential losses and fraud risks outside of user assets, realizing the security concept of "protecting before anomalies occur."
Recently, the OKX Wallet has also launched a new Security Landing Page Audit Report and publicly disclosed its security protection system, allowing users to view it anytime, anywhere.
In this world, protection is no longer an occasional reminder but a normalized capability: real-time risk identification, layered threat interception, early interception of potential losses, making security a perceptible and reliable presence. By 2026, perhaps more users will pause in this enchanting yet complex city, not out of fear, but because of visible guardianship, to explore the infinite possibilities of the on-chain world.
This article is contributed content and does not represent the views of BlockBeats.
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia






