$500 million lesson not to let PDF phishing attacks happen to you
Serpent, Web3 Security Practitioner
原文编译:0x711,BlockBeats
According to The Block, Axie Infinity employees received and downloaded a job offer as a PDF file that led to The theft of $540 million in assets in The March attack on The Axie Infinity Side Chain Ronin Bridge. The document contains a virus, resulting in information leakage.
As the amount of money in the crypto world increases, phishing attacks are becoming more common. In October last year, AnubisDAO also suffered a theft of $60 million due to SAFT protocol, which was suspected of receiving PDF files. So how to detect and prevent PDF document phishing attacks?
Serpent, a Web3 security practitioner, has combed through this hack on its social networking site. Hackers steal assets by tricking victims into clicking on executable scripts disguised as PDFS. BlockBeats has translated the tweet below.
Fake file extension scam warning
Hackers are changing file extensions to disguise malicious files as PDFS and targeting artists, influencers and project owners. The principle is as follows:
Case study: crypto artistTARSIUSReceived a delegate message and a zip package that purportedly contained "customer requirements, examples, sketches, etc." When the artist opened the compressed package, the ordinary commission turned sour.
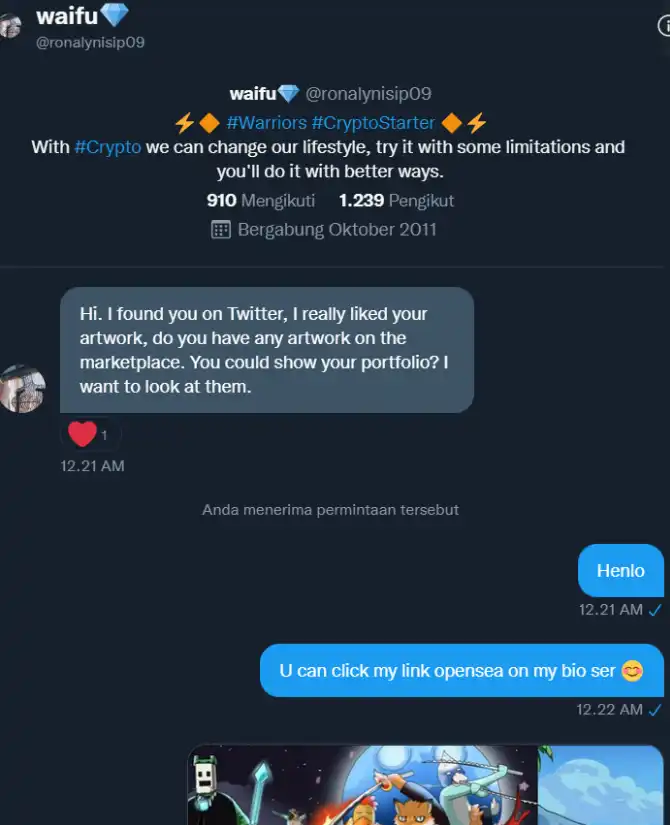
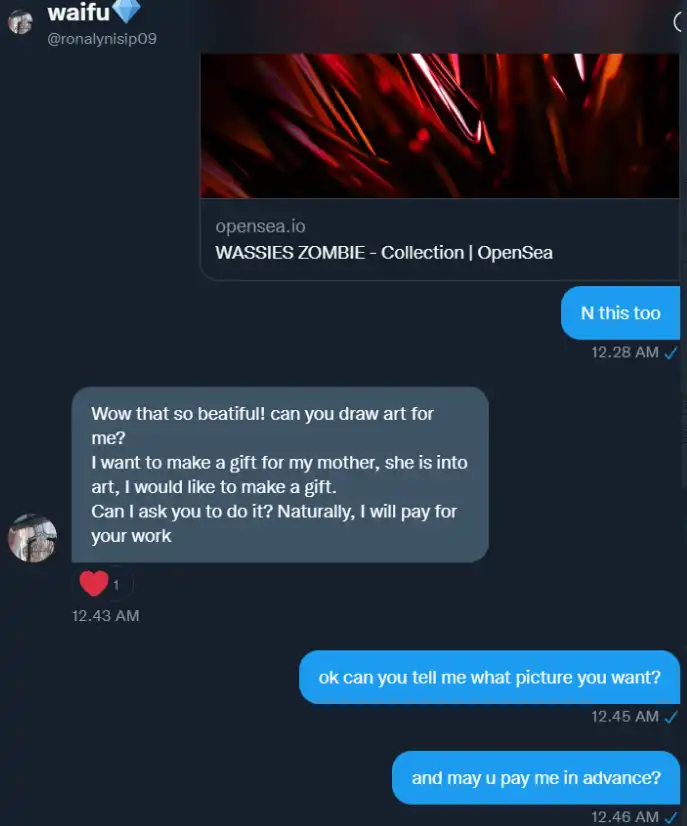
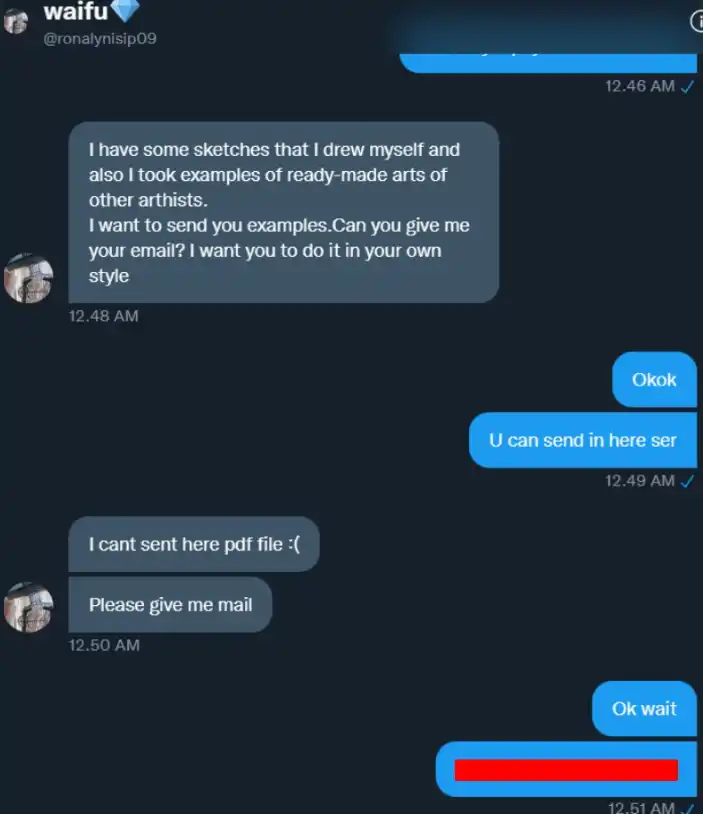
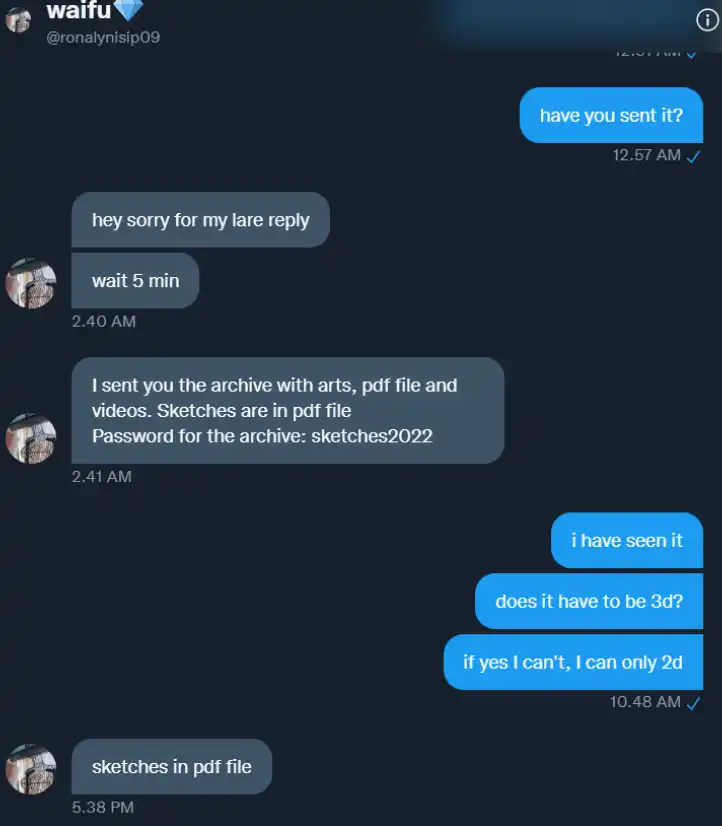
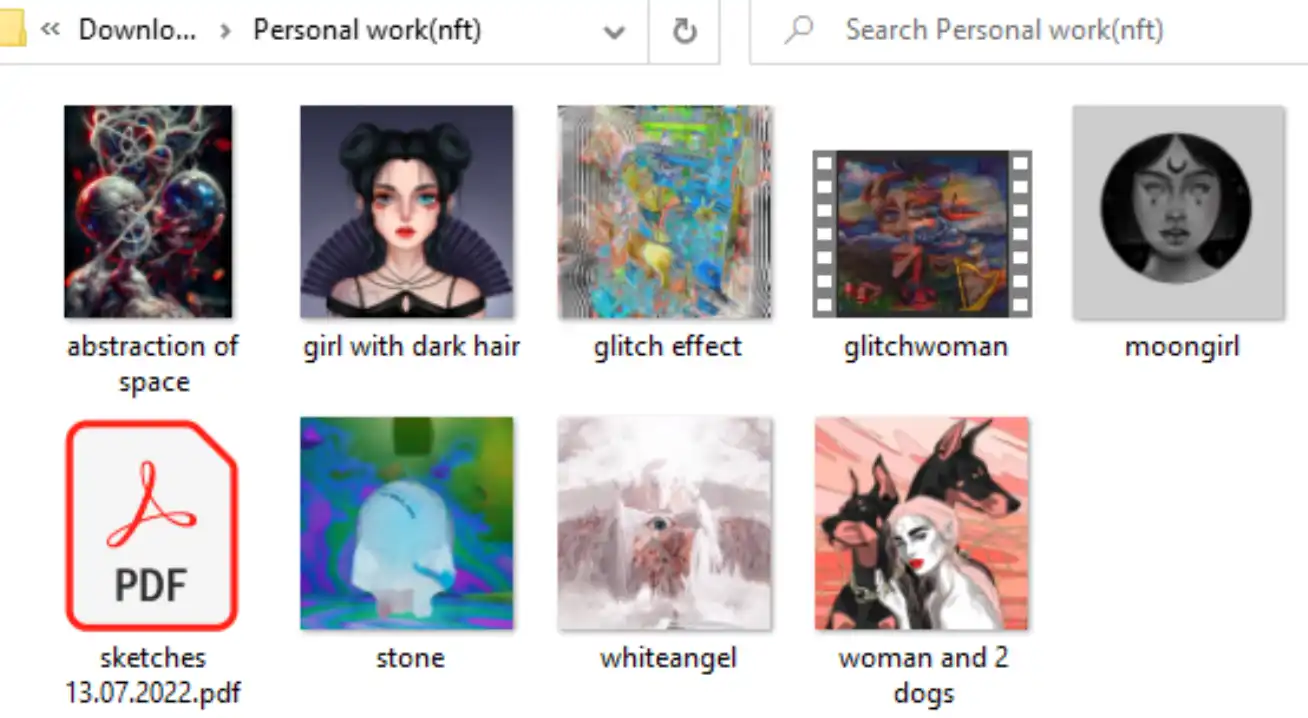
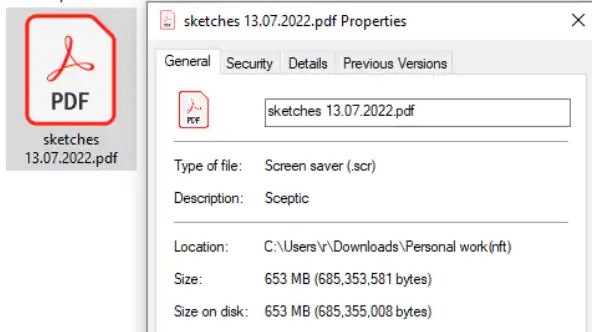
When we open the zip file, we can see the sample provided, as well as a PDF file containing the "customer" sketch, but this is no ordinary PDF file.It is actually a screensaver (.scr) file, which is an executable script disguised as a PDF file.
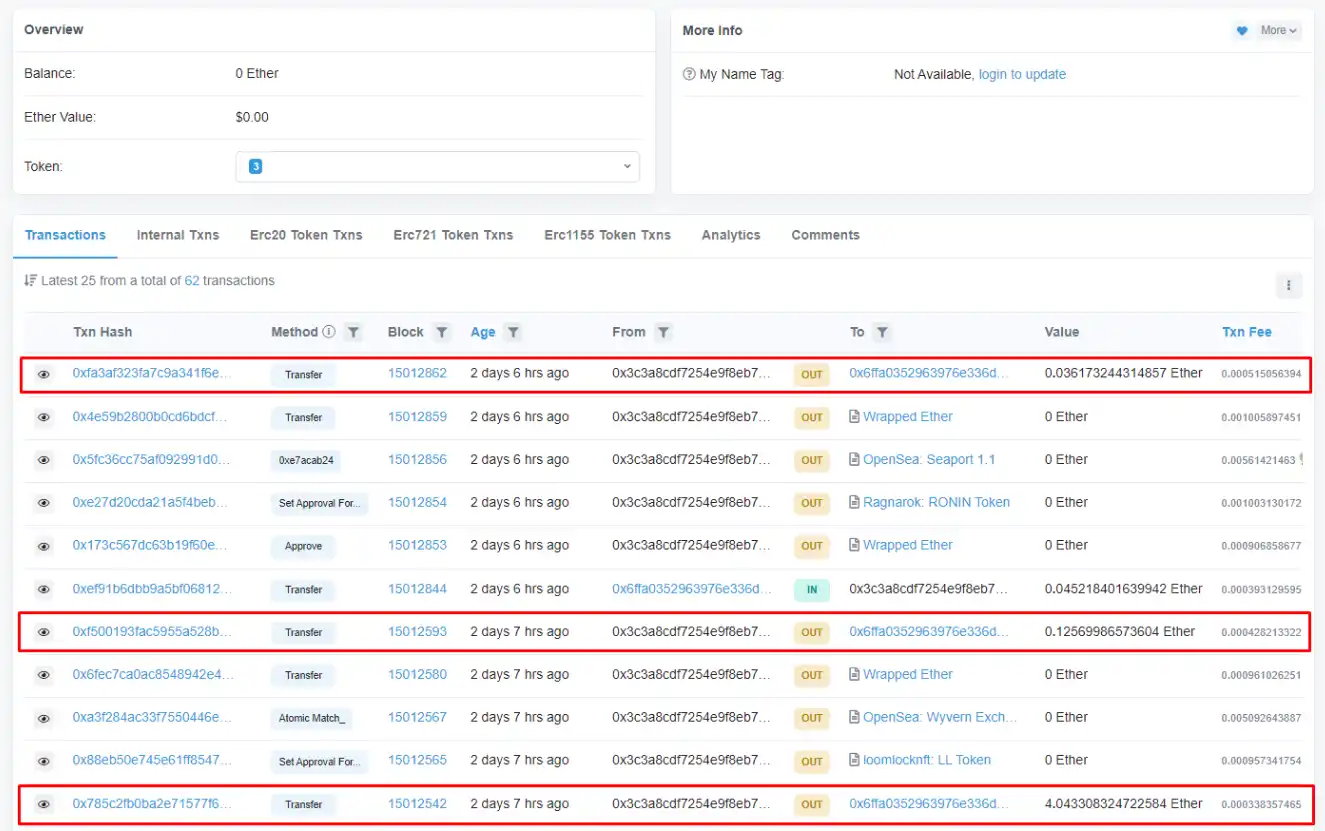
艺术家打开 PDF 文件查看草图后,他的所有 NFT 都被上架并出售,他所有的 ETH 都被转移到了骗子的钱包。
篇幅所限,本文只列举受害者部分交易。
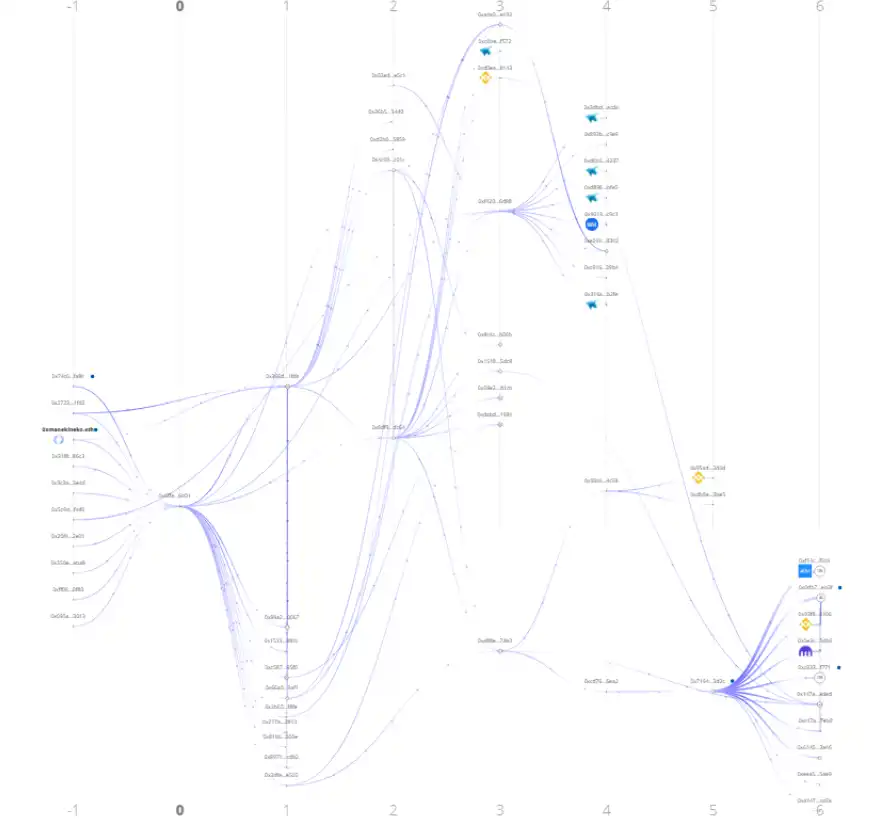
So how did the hackers get away with it? He changed the file extension and added.pdf at the end, then changed the file icon to the PDF icon. He also added to the confusion by padding the file with junk code larger than the size of the virus file itself.
Artists are not the only targets of this scam. Recently, kols, promoters and project owners have been targeted and many have lost control of their wallets and accounts, wiping everything out completely.
This is an old Web2 fraud strategy that applies to any and all file types.
How can this be avoided?
1. Do not download or open random files at will;
2. Always check the file type;
3. Research and learn basic Web2 security.
If you need to open any files, put them on Google Drive and view them there, or use a virtual machine. I personally use both.
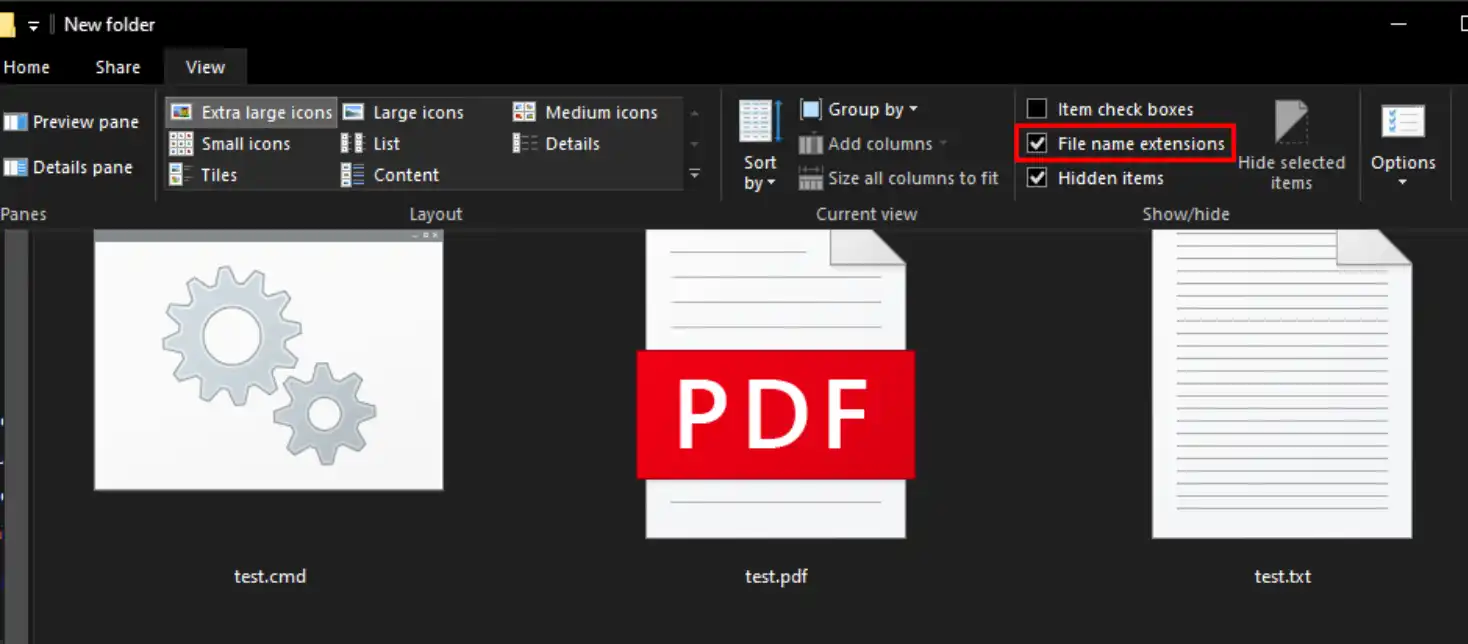
You can enable the file type extension by clicking View at the top of File Explorer, and then enabling File Extension. This will display the file extensions for all files. (This feature is turned off by default.)
An.scr file is an executable file that can run any code, and it's basically an.exe file. How will they damage your wallet in this way? Well, from this point on, we can assume that your entire PC is under attack.
你所有的 cookies、密码、扩展数据,所有的东西,都被窃取了。例如,他们可以将您的 MetaMask 插件更改为经过修改的恶意版本,或者更简单地说,他们可以等待您登录并访问您的 MetaMask,他们将拥有一切。
解决办法有很多,但如果你确实中招了,你可以假设你的电脑受到了损害。我建议重置它,创建一个新钱包,并更改所有密码。
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia
 Related Articles