A job Offer worth $540 million
How a fake Job Offer Took down the world's most popular Crypto game
Ryan Weeks, The Block
0x9F, BlockBeats
On March 29, Axie Infinity Side Chain Ronin posted that 173,600 ETH and 25.5 million USDCS were stolen from the verification node, and Ronin Bridge and Katana Dex were suspended (both have now been restored). On April 27, Ronin reported a security breach in which attackers stole funds by taking control of five of the nine verified nodes' private keys. Only one Sky Mavis employee was mentioned in the report as the victim of a phishing attack, which allowed the attacker to penetrate the Sky Mavis IT infrastructure and gain access to the verification node.What was the exact fishing attack that led to Axie Infinity's worst mistake ever? The Block has exclusive access to The details. BlockBeats has The following translation:
It's hard not to notice the resume of a senior engineer at Axie Infinity. The engineer's interest in joining a fictitious company led to one of the crypto industry's biggest hacks.
Ronin is a side chain of Ethereum and the cornerstone of the P2E game Axie Infinity. It was in an attack in MarchIt lost $540 millionCryptocurrency. Although later this incidentAlleged links to the North Korean hacking group Lazarus, but full details of how the flaw was exploited have not been disclosed. The Block can now reveal that,A fake job AD proved Ronin's undoing.
A senior engineer at Axie Infinity was tricked into applying for a job at a company that did not, in fact, exist, according to two people with direct knowledge of the matter, who spoke on the condition of anonymity because of the sensitivity of the matter.
Axie Infinity is so large that at its peak, workers in Southeast Asia could pass itMake money to make a living.Last November, it owned 2.7 million daily active users, the weekly in-game NFT transaction volume is 214 million dollars.Since then, though, both numbers have fallen sharply.
Earlier this year, representatives from the nonexistent company approached employees at Axie Infinity developer Sky Mavis and encouraged them to apply for jobs, according to people familiar with the matter.These contacts were made through linkedin, the professional networking site.After several rounds of interviews, a Sky Mavis engineer was offered a very lucrative job.
The fake "offer" came in the form of a PDF, which the engineer downloaded, allowing the spyware to infiltrate Ronin's system.From there, hackers were able to attack and take over four of the nine validation nodes on Ronin's network, missing only one validation node to gain full control.
Published on April 27thA post summarizing the attackIn, Sky Mavis said: "Employees were continuously subjected to advanced spear-phishing attacks from various social channels and one employee was compromised. This employee no longer works at Sky Mavis. The attacker successfully used this opportunity to infiltrate Sky Mavis's IT infrastructure and gain access to the verification nodes."
Verification nodes perform various functions in the blockchain, including creating transaction blocks and updating data prognostics.Ronin uses a so-called "proof of authority" system to sign off on deals, centralizing power in the hands of nine trusted actors.
Blockchain analytics firm Elliptic in & NBSP;An April blog post about the incident"If five of the nine authentication nodes approve, the funds can be transferred out. The attacker managed to get hold of the private keys belonging to five of the authentication nodes to steal the crypto assets," explains.
But after successfully breaking into Ronin's system through fake job ads, the hackers took control of only four of the nine verification nodes. They also need another validation node to gain control.
Sky Mavis After the said.The hackers managed to pull off the heist using the Axie DAO.Axie DAO is an organization that supports the gaming ecosystem. In November 2021, Sky Mavis asked DAO for help handling heavy transaction loads.
"Axie DAO allowed Sky Mavis to sign various transactions on its behalf. This was terminated in December 2021, but access to the permitted list was not revoked. Once an attacker entered the Sky Mavis system, they were able to obtain signatures from the Axie DAO verification node."
A month after the attack, Sky Mavis had increased its number of verified nodes to 11, and stated in the blog post that its long-term goal was to have more than 100.
Sky Mavis declined to comment on how the attack was carried out, and linkedin did not respond to multiple requests for comment.
Earlier today, ESET Research Published a surveyIt showed that North Korea's Lazarus abused linkedin and WhatsApp to target aerospace and defense contractors by posing as recruiters. butThe report did not link the technique to the Sky Mavis attack.
In early April, SkyMavis raised money ina financing round led by Binance.150 million dollars. The proceeds will be used along with the company's own funds to repay customers affected by the breach. The companyRecently said, will start returning money to users on June 28. Ronin Bridge was suspended because of the attackIt was restarted last week.
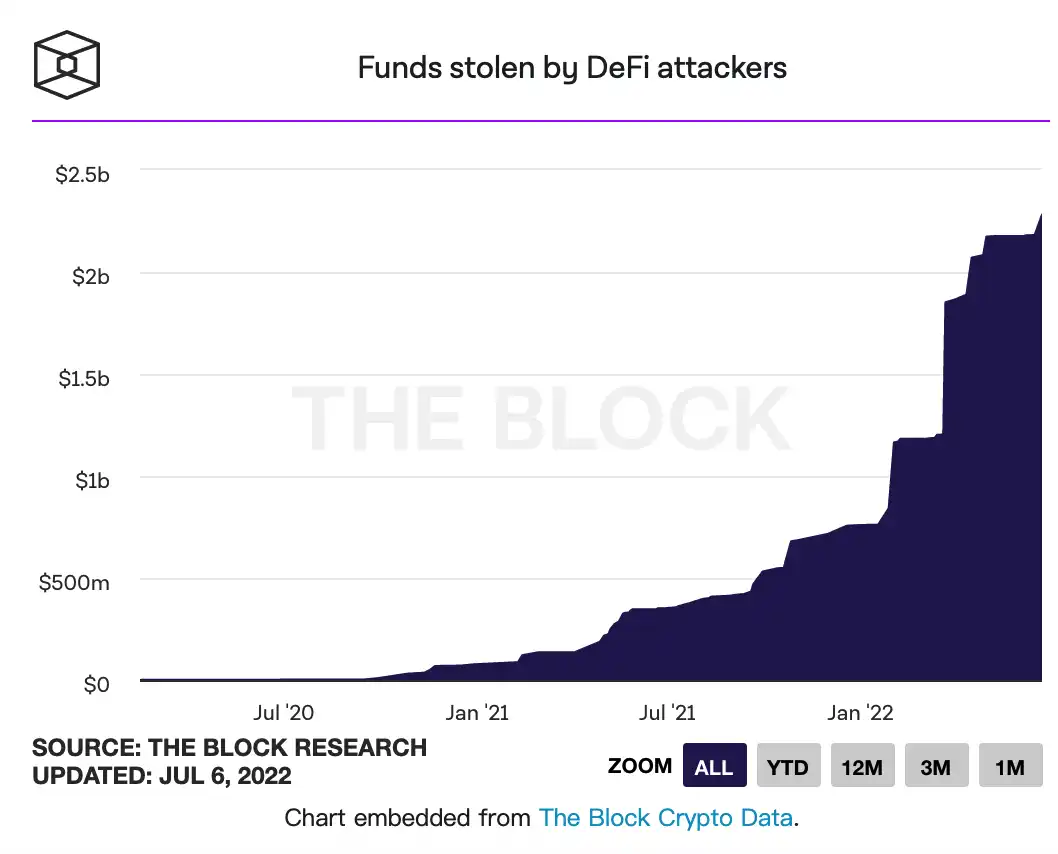
According to & have spentData from The Block ResearchDisplay,DeFi attacks have accelerated rapidly this year, with losses totaling more than $2 billion.On January 1, it was still $760m.
The original link
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia

 Related Articles