Has been at the top of the Ethereum executive layer bug bounty list for a long time, Samczsun's white hat hacker road
Original title: "How was samczsun, the top white hat hacker in the encryption industry, born?" "
Original author: Gu Yu, chain catcher
"U up?" (Are you awake?) < br>
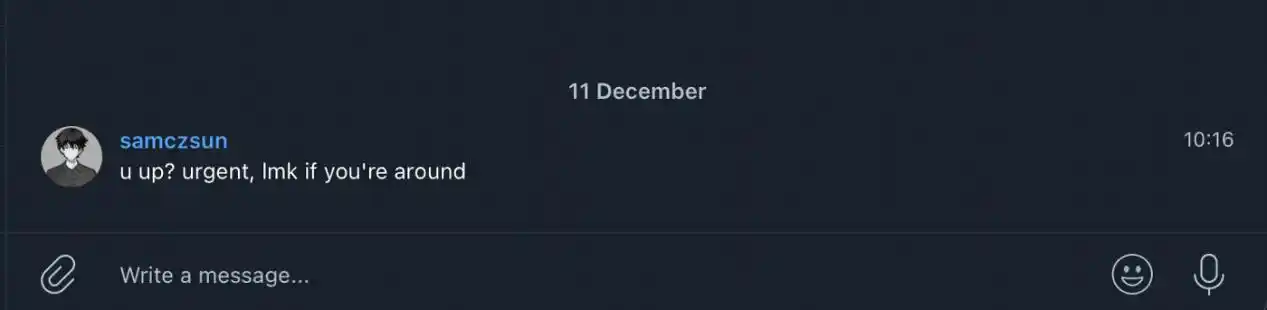

This inquiry from samczsun is one of the most feared news for any DeFi project party, because it probably means that samczsun has discovered a serious loophole in the project’s smart contract, and user assets may be stolen by hackers at any time .
In the encrypted world, smart contract loopholes in various protocols are common, and they have become attractive "fat meat" in the eyes of hackers. According to Footprint Analytics statistics, at least 90 DeFi projects will encounter various attacks in 2021, with an initial loss of more than US$1 billion, bringing great losses to ordinary users. However, while hackers act recklessly, there are also many white-hat hackers helping project parties discover smart contract vulnerabilities in advance.
Samczsun is the most well-known white hat hacker in the encryption industry, bar none. In the past few years, samczsun has helped at least 20 projects discover system vulnerabilities in advance and avoided hundreds of millions of dollars in losses through private messages to project parties, including Sushiswap, ENS, Rari, Tokenlon, etc.
Samczsun’s official identity is Paradigm’s research partner, a well-known encryption venture capital institution, focusing on Paradigm’s portfolio companies and research on security and related topics. Almost all of his public statements are reports and analysis of encryption project vulnerabilities , in order to protect the healthy development of encryption ecology.
Although samczsun has stated that he will give priority to reviewing portfolio companies planning to release new codes, most of the projects he disclosed vulnerabilities are not Paradigm's portfolio projects, such as Sushiswap, ENS, ForTube, Tokenlon, etc., which also makes him a One of the most influential figures who have contributed the most to the security field of the DeFi ecology and even the encryption industry.
Dragonfly Capital partner Haseeb said in a recent interview that he thinks samczsun is the smartest person working on Web3. Another Paradigm partner, Dan Robinson, called him the Batman of the encryption industry. Whenever a significant amount of money is at risk in the crypto ecosystem, the bat signal is sent and samczsun comes in to help save the day.
So how did samczsun become one of the top white hat hackers today? In this article, Chain Catcher will roughly sort out and summarize his past experience through public information.
Judging from samczsun's social media profile, his earliest network activity was in November 2014, when he joined Github in that month and made 114 contributions in November-December.
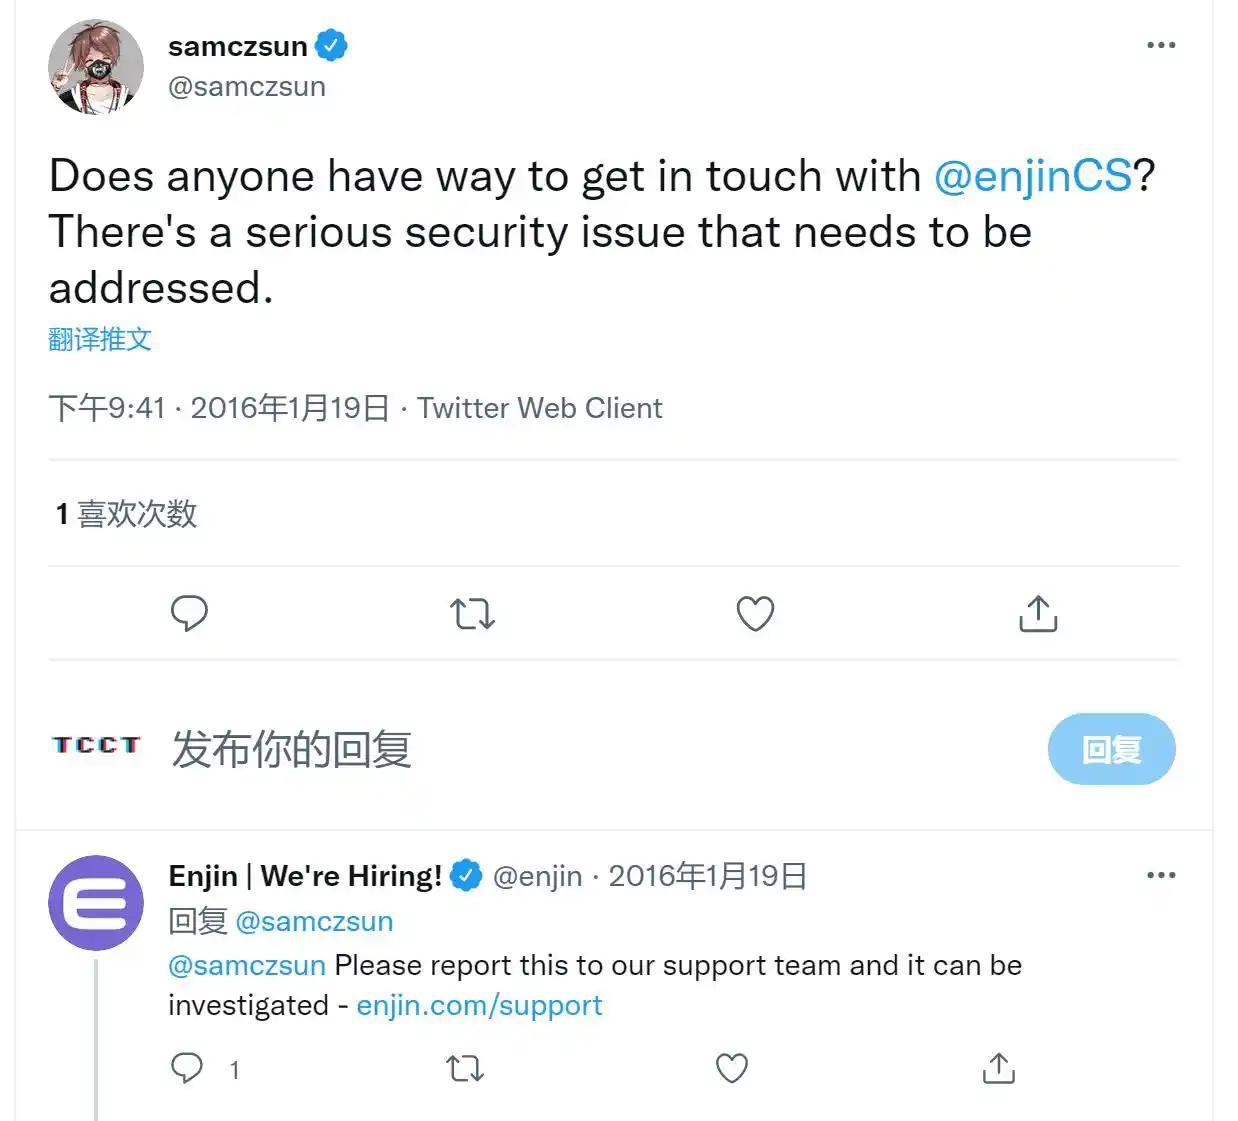
Samczsun's earliest traceable vulnerability mining record was in January 2016, when he tweeted @Enjin's official Twitter, saying that there were serious security issues that needed to be resolved, and then Enjin's official tweet responded and provided a report to submit Link. This Enjin is now the popular NFT game platform Enjin, but at that time the project had not yet entered the encryption and NFT track.
In 2017, samczsun submitted multiple project vulnerabilities on the bug bounty platform Hackerone, including the Indian version of Meituan Zomato, legal contract analysis company Legal Robot, and published many vulnerability analysis articles on his blog.
Samczsun’s first public investigation into DeFi protocol vulnerabilities was in July 2019, when he disclosed to the 0x protocol a smart contract vulnerability that allowed malicious actors to spend their assets on behalf of any approved 0x contract Externally Owned Accounts (EOAs) created valid orders, and the project had to shut down the protocol to patch the bug and deploy the 0x v2.1 smart contract from scratch. For this breach, samczsun received a $100,000 bounty.
Samczsun has officially started the road of white hat hacking since then, and quickly became popular in the DeFi industry with quite high-yield vulnerability research.
In the following year, with the "Summer of De-Fi" boom in 2020, Samczsun discovered potential vulnerabilities in many encryption projects such as ENS, Livepeer, bZx Network, and Curve Finance.
Among them, Curve Finance's loophole can allow anyone to use the loophole to exhaust the smart contract, and the ENS loophole can enable ENS users to regain ownership after transferring ownership to others in a certain way. The loopholes that have a significant negative impact on project development show the great contribution of samczsun.
“A common misconception in building software is that if each component in a system is individually verified to be safe, then the system itself is also safe. This belief is best illustrated in DeFi, where , composability is second nature to developers. Unfortunately, while combining two components may be safe in most cases, it only takes a single vulnerability to cause serious damage to hundreds or even thousands of innocent users. Economic loss.” Samczsun concluded after discovering many vulnerabilities in DeFi projects, “Safety components can also come together to make something unsafe.”
At the beginning of 2020, samczsun also initiated grants on the Gitcoin platform and became the object of Gitocin's fifth round of grants with the most funds raised. During the same period, samczsun also joined the encryption security company Trail of Bits as a security engineer.
As of September 2020, samczsun, already well-known in the field of DeFi security, was invited by the founder of Paradigm to become a research partner of the investment institution to "help assess the security status of potential portfolio companies and assist the current portfolio company, to promote the overall security of the Ethereum ecosystem.”
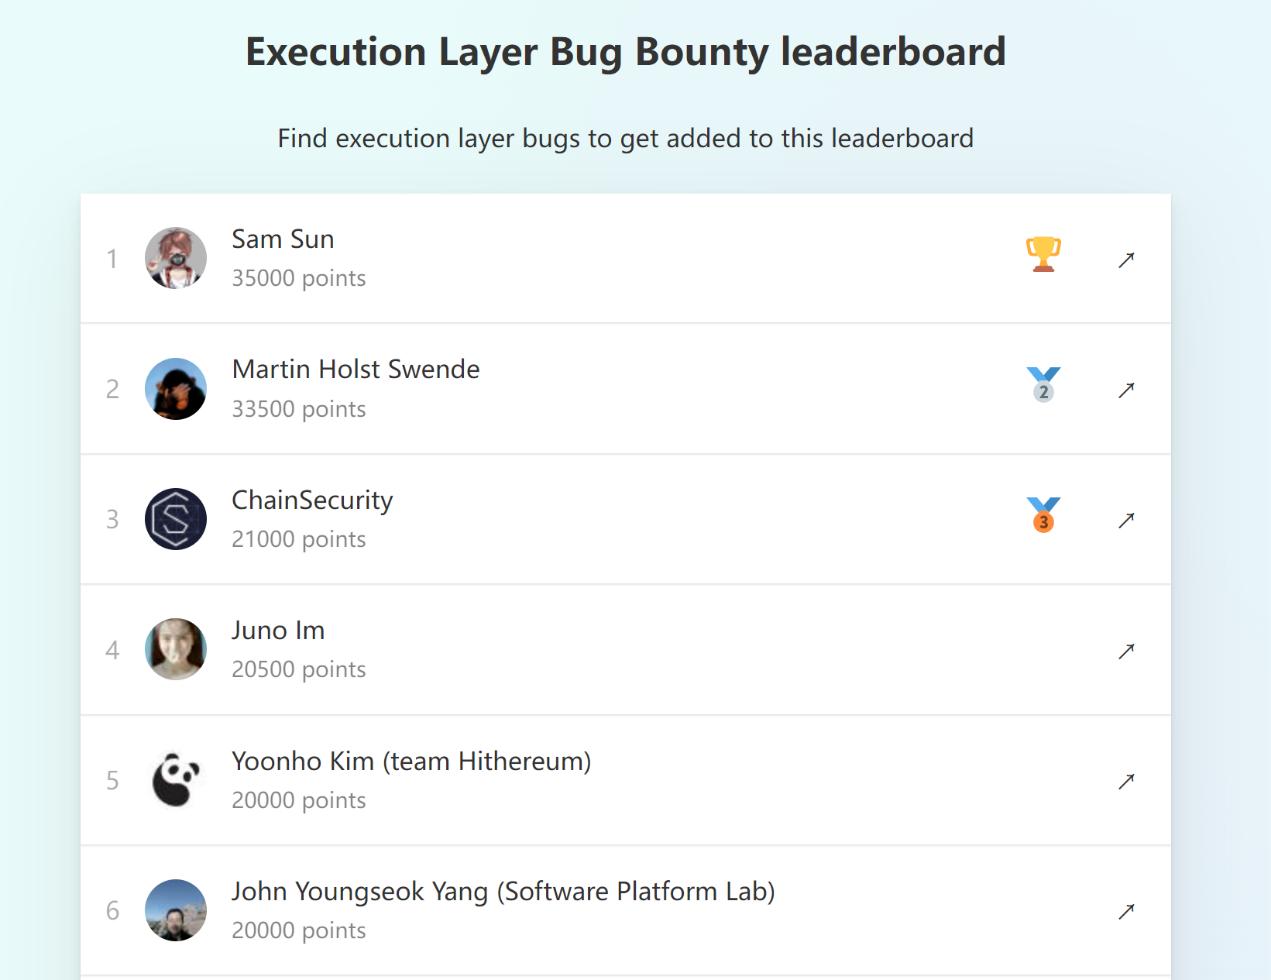
Ethereum execution layer bug bounty list
Since then, samczsun has continued its practice of vulnerability disclosure, involving Alpha Homora, DODO, Rari, Tokenlon, ForTube, BendDAO and other projects, among which the Rari code vulnerability may lead to the theft of all borrowable assets in the Fuse pool. Samczsun also ranks first in the Ethereum executive layer bug bounty list published by the Ethereum Foundation for a long time. In addition, samczsun also helped project parties such as dYdX and Gelato Network deal with vulnerability incidents urgently.
Among them, the case that made samczsun most famous was the MISO vulnerability incident, which helped the project avoid a loss of up to 350 million US dollars.
On August 17, 2021, when samczsun noticed that the SushiSwap IDO platform MISO was conducting the largest IDO (BitDAO) in history, he then opened the MISO smart contract on Etherscan, and soon found that the initMarket function has no access control, The function called by initAuction also does not contain access control checks.
Specifically, this vulnerability will cause MISO to incorrectly handle the failed transaction in the Dutch auction, that is, the smart contract will not reject the transaction exceeding the upper limit of the auction Token, but will refund the user after the auction ends. Thus, an attacker could exploit a vulnerability in the MISO platform to bid for free and get refunded for the difference between the submitted amount and the current bid, until all funds in the contract are exhausted. In other words, the bug put more than 109,000 ETH (worth $350 million at the time) raised by the project at risk of being stolen.
After realizing the seriousness of the vulnerability, samczsun contacted the Sushi team and held a conference call to inform them of the specific vulnerability, and then communicated closely with the project party to deal with the funds in the smart contract urgently, and finally resolved the problem within three hours crisis. Afterwards, Samczsun received a bounty reward of 1 million USDC from the Sushi team.
In an interview with Immunefi after the fact, samczsun used "a strange combination of excitement and fear" to describe the mood of discovering the vulnerability. "Excitement, that you've just found what you've been looking for. Fear, because the clock is ticking and every second that passes, someone else finds the same mistake. My heart rate goes up in direct proportion to the amount at stake."
After this battle, samczsun's influence has expanded from the security circle to the entire encryption industry, becoming the most well-known white hat hacker and encryption security researcher in the industry.
However, samczsun's outstanding contribution also vaguely implies an uneasy and cruel fact that the encryption security ecosystem is still quite fragile, although a few white-hat hackers like Samczsun choose to disclose to the project party with a high sense of industry responsibility and morality , but most hackers choose to actively attack after discovering vulnerabilities to achieve more profits.
This has also led to various security incidents that have occurred in the encryption industry one after another this year, such as the theft of more than 600 million US dollars from the Ronin cross-chain bridge, and the theft of 80 million US dollars from Rari Capital (although samczsun had previously reported a major vulnerability in the project and fixed it. ), the Beanstalk Farms theft of more than $80 million and other incidents have repeatedly impacted the confidence of the encryption community.
All the contributions of samczsun are a blessing to the industry, but it also reflects the tragedy of the industry.
Original link
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia
 Related Articles