Demystifying the New NFT Airdrop Scam, Beware of False Offers Stealing Your Assets
Original title: "Understanding the New NFT Airdrop Scam in Three Minutes: Stealing Assets Through False WETH Quotes"
Original Author: 0xfoobar, NFT &MEV Developer
Original compilation: The Way of DeFi
“My wallet suddenly got an airdrop of an unknown NFT collectible, and then someone made an offer of 1 WETH. What's going on? Is it safe to accept it?"

Long story short, these are scams and you cannot profit from the interaction. Now, Let's understand how these scams work!
The way OpenSea works is to transfer your NFT or WETH through "authorization", and "authorization" is a special intelligence that you call directly on the Token contract contract function. It says:
" Token Contract, please allow my funds or JPG for this market contract. ”
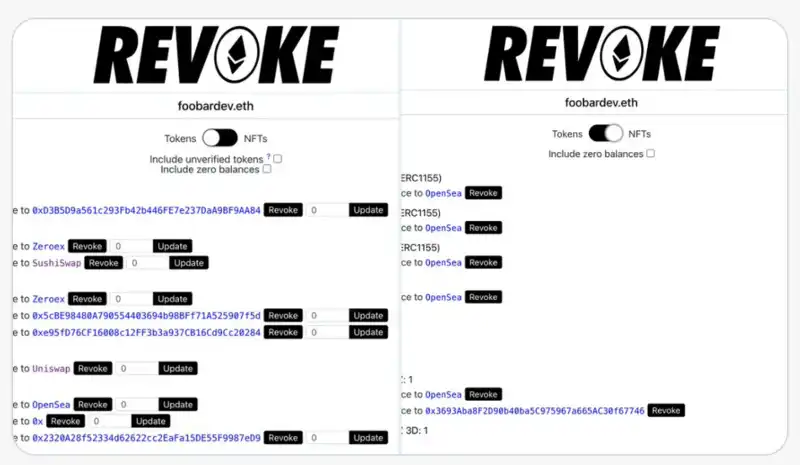
This is dangerous! But only in one direction. If the marketplace is malicious, it can steal your funds and JPGs. However, if the funds/JPGs are malicious, they "can't" steal your market.
A poorly designed marketplace may have a loophole that allows one authorized collection to steal another authorized collection. That's why we only use robust, well-tested sites.
Here is an example of an attack using the old Wyvern contract used by opensea:

Therefore, you can only approve external contracts that use funds/JPG by calling the funds/JPG contract.
Instead of calling an external contract.
This is why in theory it is "safe" to interact with a malicious contract, provided your transaction goes directly to the malicious contract and you don't send any raw ETH to the payable function.
But please be careful not to try this dangerous operation yourself.
Of course, danger occurs when people think they are interacting with an external contract, but are actually interacting with their money/JPG contract.
There will be a website that will pop up and say to you: "Click here to activate your ape", but the wallet transaction actually says "SET APPROVAL FOR ALL" (Approve all permissions).
Under the influence of a combination of drunk/high/drowsy/fomo, people will sign up to give away their life savings to others.
So if hackers can't get control of your wallet or assets, what's the plan for these fake NFT offer games?
The malicious actors used several attack schemes:
- Offer acceptance will resume when you approve the opensea marketplace contract to use your NFT, then try to accept that offer. The error message will contain a URL that, if you visit the website, will try to get you to sign a malicious transaction.
- NFT is a kind of proxy contract, which can be replaced with different implementation logic later.
The following is an address that receives dust transactions from 260 different addresses, each of which created a proxy contract to masquerade as a unique collection .
These bad actors have a low hit rate, so for gas optimization they will use a single implementation contract with heavy NFT code logic, And deploy many lightweight agents that appear to be independent collections.
Here's more about proxy mode.
Some people believe that recent NFT proxy deployers have developed secret functionality that allows them to steal all your NFTs if you call approve on the proxy.
For the reasons stated above, this seems to be completely wrong.
Gas optimization is the most probable proxy usage assumption.
The OpenSea frontend is pretty closed in terms of the collection functions it calls, so most of the bogus WETH offers are just to lure you to a phishing site.
To summarize:
False WETH Quote will allow you to approve the sale of that NFT, but when you try to accept the offer, the transaction will resume. This will cause you to waste gas fees, and at the same time revert messages on Etherscan to lure you to phishing websites.
Please protect your wallet!
Original link
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia
 Related Articles