SlowMist Recaps the $615 Million Largest Cryptocurrency Hacking in History
Original title: " Loss of more than 610 million US dollars - Ronin Network hacked analysis "
Original author: SlowMist Technology
On March 29, 2022, Axie Infinity side chain Ronin Network issued a community warning, Ronin Network A security breach occurred, and a total of 173,600 ETH and 25.5 million USDC were stolen from Ronin Bridge, resulting in a loss of over US$610 million. The SlowMist security team immediately intervened in the analysis and shared the analysis results as follows.

Related information
Ronin is a sidechain of Ethereum, specially created for Axie Infinity, the leader of chain games. It claims to be developing in the direction of "the most commonly used Ethereum sidechain for NFT games". It is understood that Axie Infinity's team, Sky Mavis, wanted a reliable, fast, and cheap network to guarantee the development of the game. They needed a game-first scaling solution that would not only stand the test of time, but also meet the high demands of the game's rapid growth. Thus, the Ronin chain came into being.
Hacker Address:
0x098B716B8Aaf21512996dC57EB0615e2383E2f96
Attack Details
< p>According to the official information, the attacker used the hacked private key to forge withdrawals, Funds were withdrawn from the Ronin bridge in just two transactions. It’s worth noting that the hack happened as early as March 23, but officials allegedly only discovered the attack after users reported being unable to withdraw 5k ETH from the bridge. The loss of this incident is even higher than that of last year PolyNetwork hack, which also stole over $600 million.
The background of the matter can be traced back to last November, At that time Sky Mavis asked Axie DAO to help distribute free transactions. Due to the huge user load, Axie DAO whitelisted Sky Mavis, allowing Sky Mavis to sign various transactions on its behalf, a process that was halted in December. However, access to the whitelist was not revoked, allowing the attacker to sign from the Axie DAO validator via gas-free RPC once they gained access to the Sky Mavis system. Sky Mavis' Ronin chain currently consists of nine validating nodes, of which at least five signatures are required to identify a deposit or withdrawal event. The attackers discovered a backdoor via a gas-free RPC node, and eventually the attackers managed to gain control of five private keys, including four Ronin validators from Sky Mavis and a third-party validator run by Axie DAO.
MistTrack
< br>
After the incident, SlowMist followed up and analyzed it immediately and in the early morning of March 30th, Beijing time 1: 09 Voice.

According to the analysis of SlowMist MistTrack anti-money laundering tracking system, the hacker had already made a profit on March 23, and transferred out the 25.5 million USDC, which was then converted into ETH.

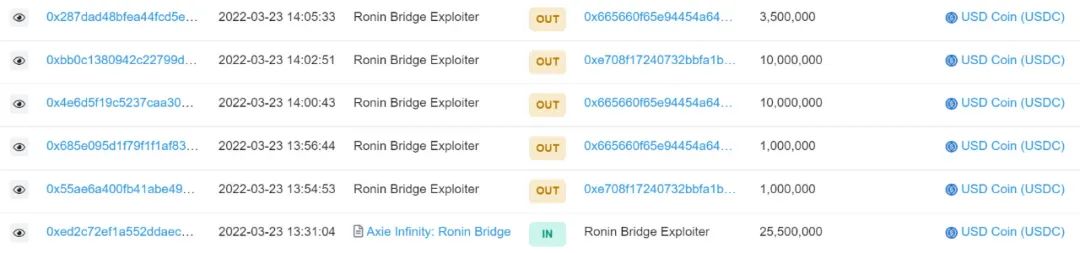
On March 28 at 2:30:38, the hackers began transferring funds.
According to the analysis of Slow Mist MistTrack, hackers first distributed 6250 ETH and transferred 1220 ETH to FTX, 1 ETH to Crypto.com, 3750 ETH to Huobi.

It is worth noting that the source of funds for the hacker’s attack was 1.0569 ETH withdrawn from Binance.

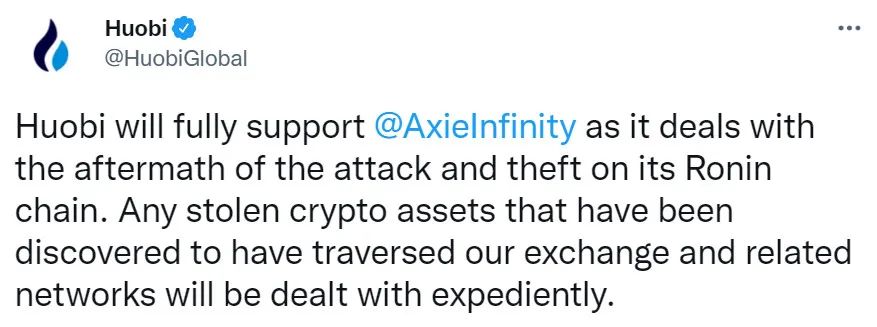
At present, the founders of Huobi and Binance have issued statements that they will fully support Axie Infinity, and FTX CEO SBF also stated in an email that they will assist in the collection of evidence.

As of now, there are still nearly 180,000 ETH staying in the hacker's address.

At present, hackers have only transferred funds to centralized platforms. Many people are discussing that hackers seem to only steal coins, but not launder them. Although it seems so, this is also a common simple and crude method of laundering coins, using fake KYC, proxy IP, fake device information, etc. Judging from the special information obtained by SlowMist so far, the hackers are not "stupid" and quite cunning, but there is still hope for recovery, and it is uncertain how long it will take. Of course, this also depends on the determination of the law enforcement agencies.
Summary
< /p>
The main reason for this attack is that the Sky Mavis system was hacked and the Axie DAO whitelist authority was improperly maintained. At the same time, we might as well speculate boldly: Do the Sky Mavis systems hold the private keys of 4 verifiers? The attacker obtained four verification node permissions by invading the Sky Mavis system, and then signed the malicious withdrawal transaction, and then used Axie DAO's whitelist permission for Sky Mavis, the attacker sent the Axie DAO validator through gas-free RPC Push the malicious withdrawal transaction to obtain the signature of the fifth verification node on the malicious withdrawal transaction, and then pass 5/9 signature verification.
Finally, here is a quote from Safe Heron (Safeheron)'s suggestion:
1. It is best to use secure multi-party computing for the private key (MPC) Eliminate single-point risk;
2. Private key fragmentation is dispersed into multiple hardware-isolated chips Protection;
3. Large capital operations should have more strategic approval protection to ensure that capital changes are handled by The main person in charge was informed and confirmed;
4. The actual time of the theft was March 23, and the project party should Strengthen service and fund monitoring.
Reference link: Ronin Network Official Analysis
Original link
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia

 Related Articles