Slow fog: A brief analysis of the BNB CrossChain Bridge black
Author: Kong, Slow Fog Security team
Source: Slow Fog technology official account
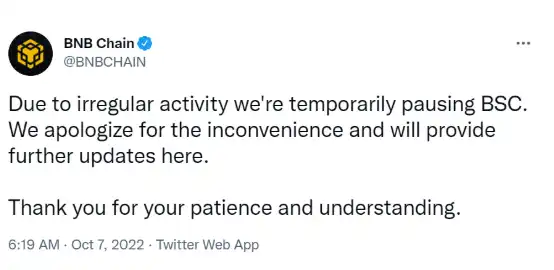
According to the Slow Fog Zone intelligence, on October 7, 2022, the BNB Chian cross-chain Bridge BSC Token Hub was attacked. A total of 2 million BNBS, worth more than $570 million, were obtained by hackers using the cross-chain Bridge vulnerability in two separate attempts. After analysis by the slow fog safety team, it will be shared with everyone in the form of brief analysis. (Note: BSC Token Hub is a cross-chain bridge between BNB beacon chain (BEP2) and BNB chain (BEP20 or BSC).)
The brief analysis of
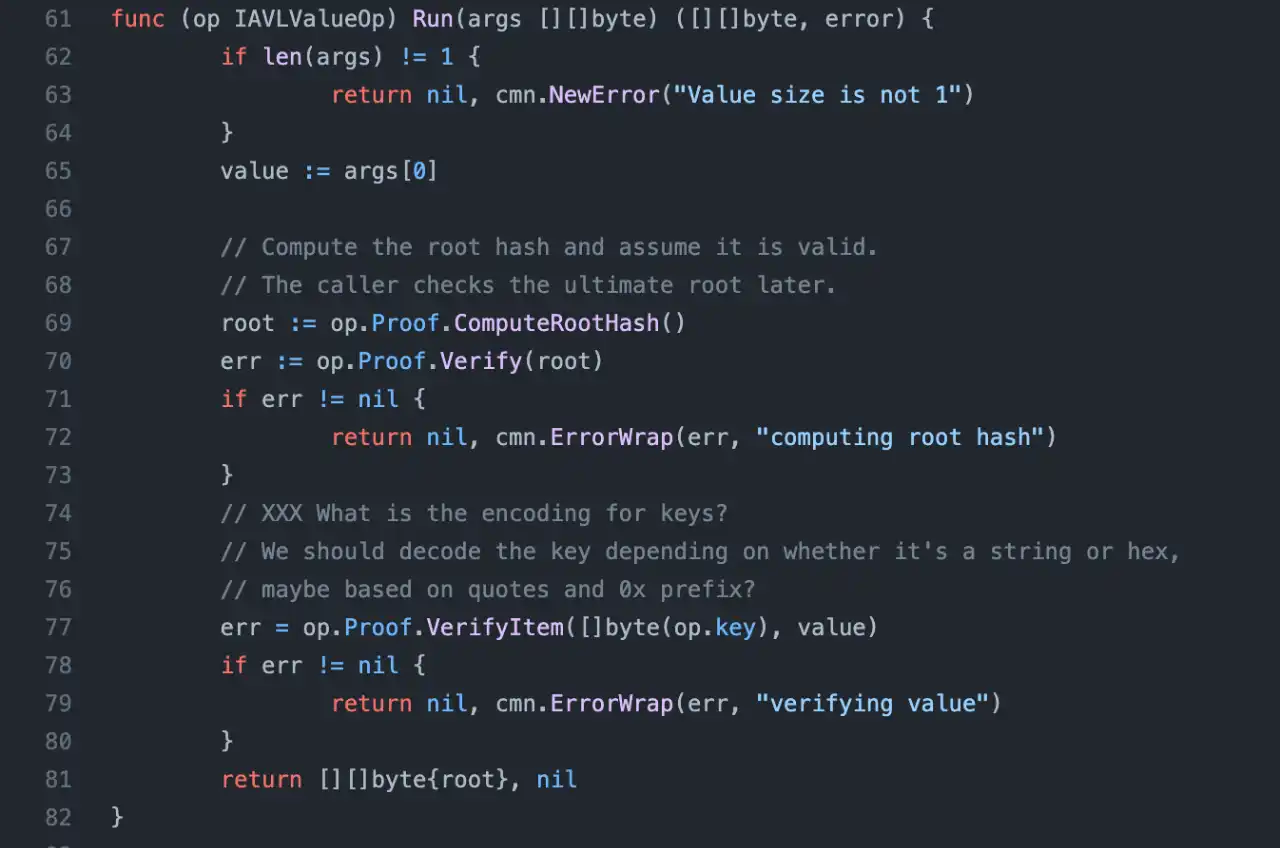
1. During the cross-chain process between BNB Chain and BSC, the pre-compiled 0x65 contract is invoked by the cross-chain contract deployed on BSC to perform IVAL tree verification on the submitted appHash, key, vaule, and proof. An IAVL tree is an AVL tree implementation that provides verifiable roots for key values.
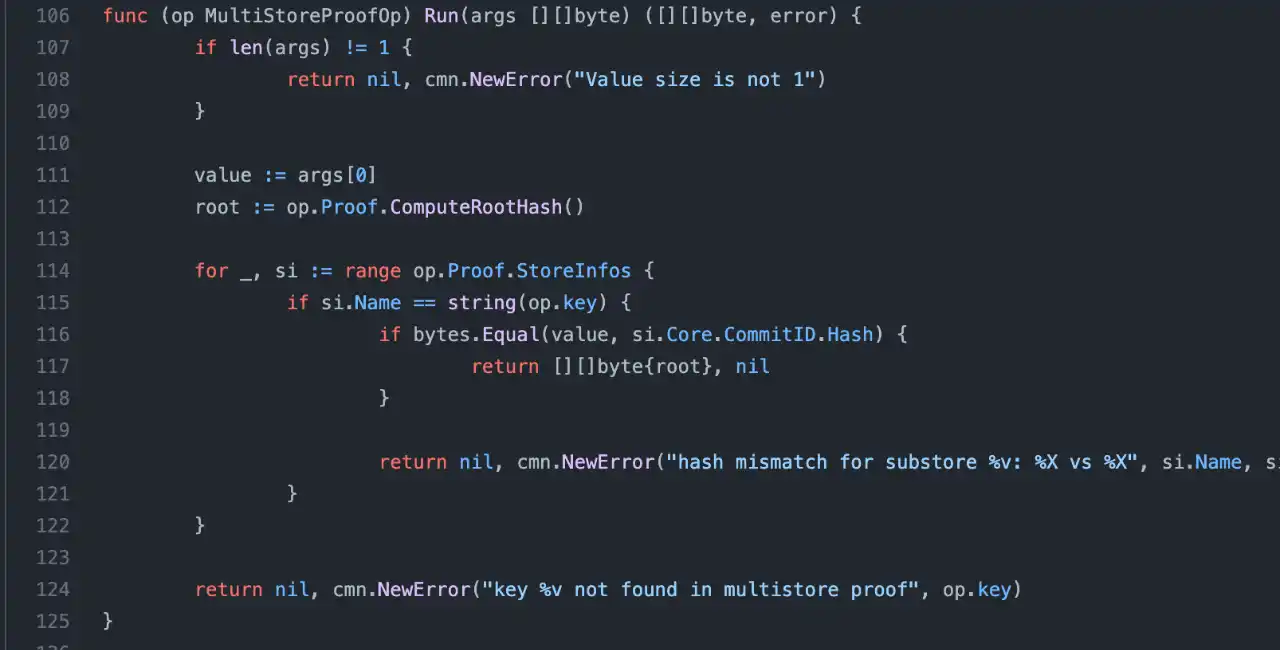
2. The verification is mainly performed by IAVLValueOp and MultiStoreProofOp. IAVLValueOp calculates roothash through ComputeRootHash and verifies it. After verification, the output roothash is given to MultiStoreProofOp, which checks to see if the obtained roothash is the same as that obtained by lightClient.
3. ComputeRootHash performs a recursive hash between leaf hash and rest path(innernode) and checks whether the right value of the last path node is the same.
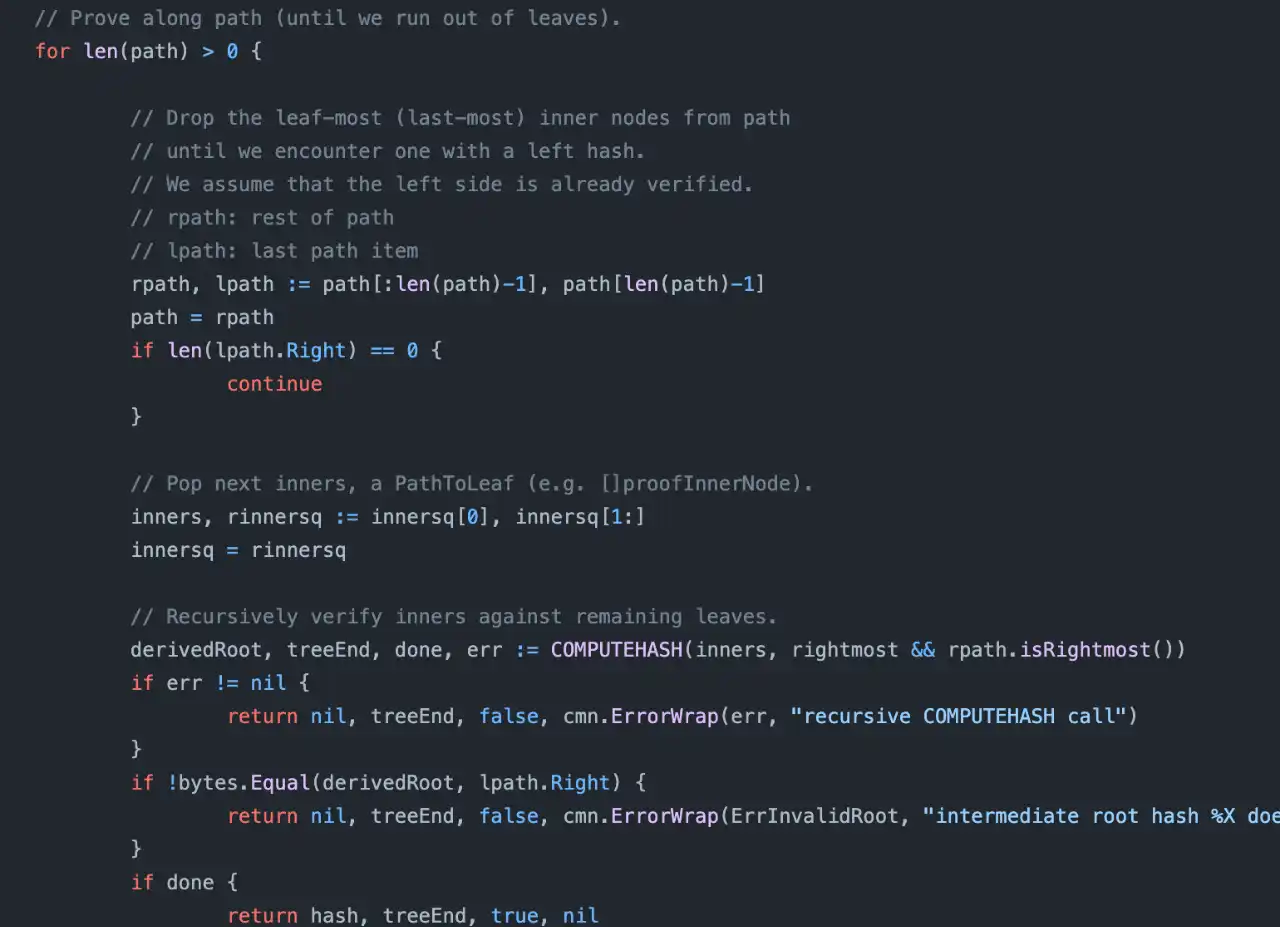
4. In the specific hash calculation of leafnode and innernode, we can see that when left is empty, the hash of leaf and right will be calculated; when right is empty, the hash of leaf and left will be calculated. However, when both left and right are present, then the hash of leaf and left is ignored and roothash will not be affected by right.
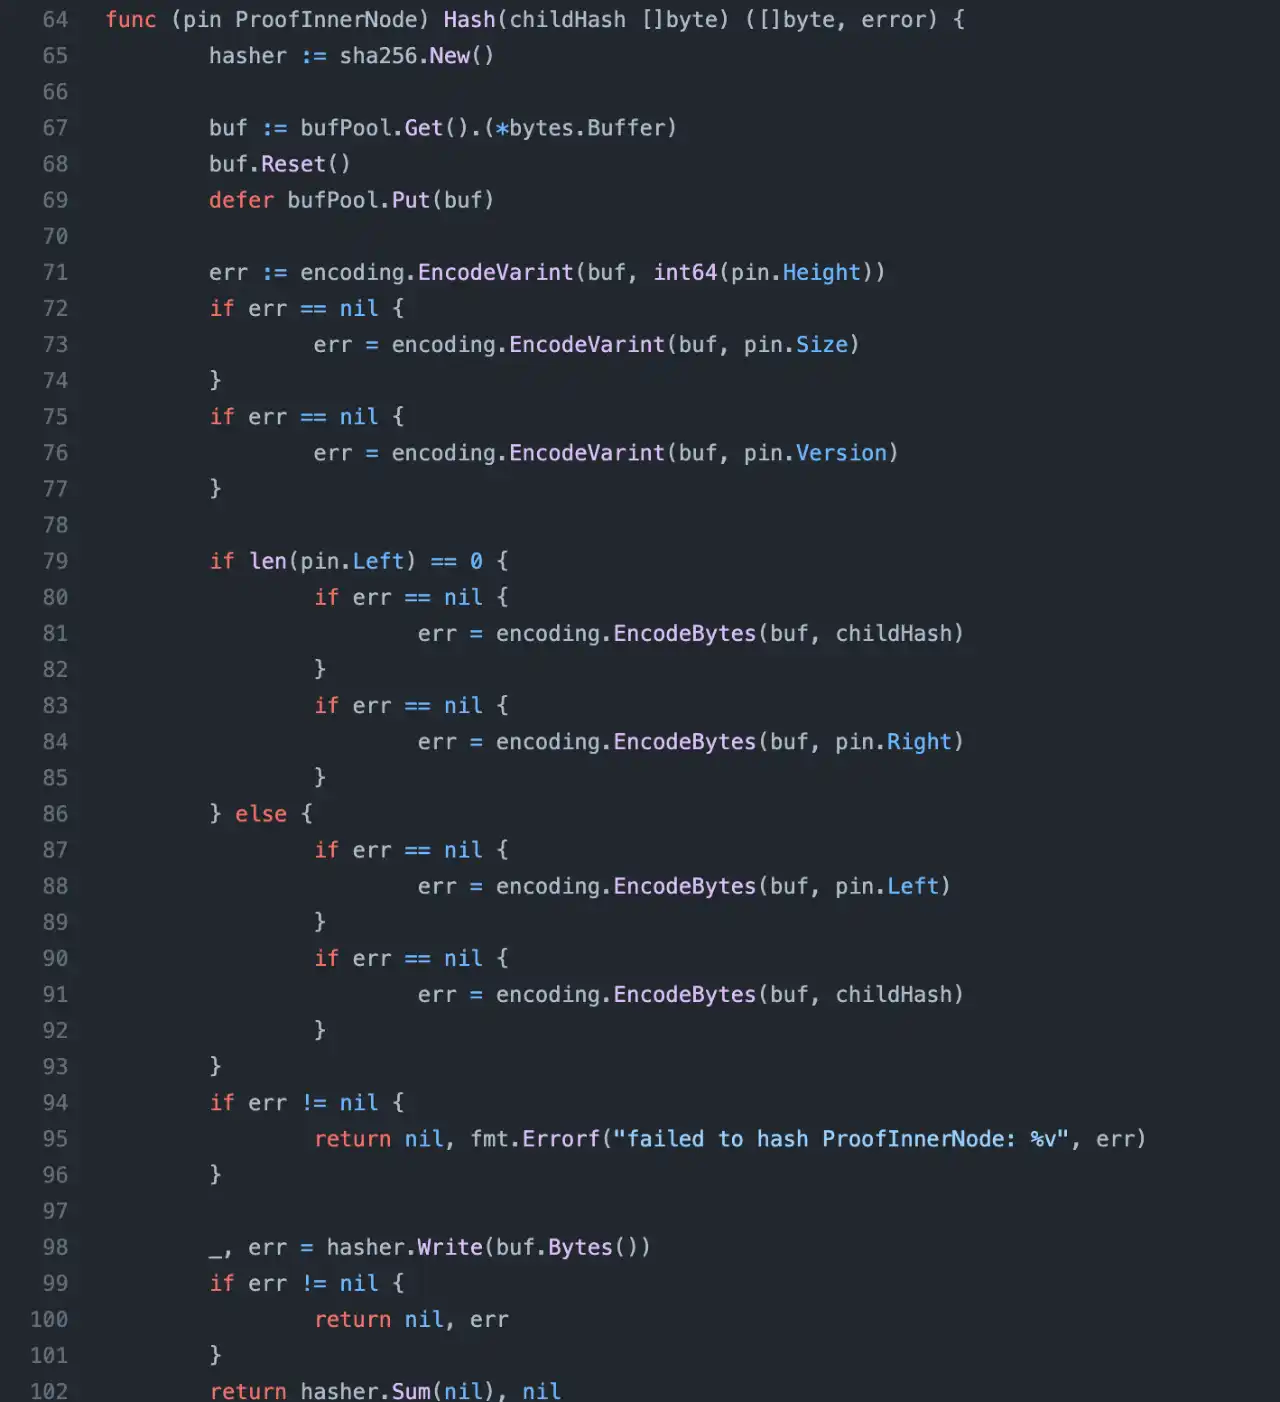
5. So we know that in path, right will be ignored if both left and right are present, and the hash of leaf and left will be returned. In the recursive hash check, the hash is checked to see if the hash matches the right of the last path node. This is where right is checked in the recursive check but omitted in the roothash calculation. So an attacker can add a hash of leaf and innernode to the path as the right of the last path node and add an empty innernode to make it verifiable. Allowing malicious data to be inserted to steal money while keeping roothash intact.
MistTrack analysis
According to MistTrack, the initial funding for the attack came from ChangeNOW.
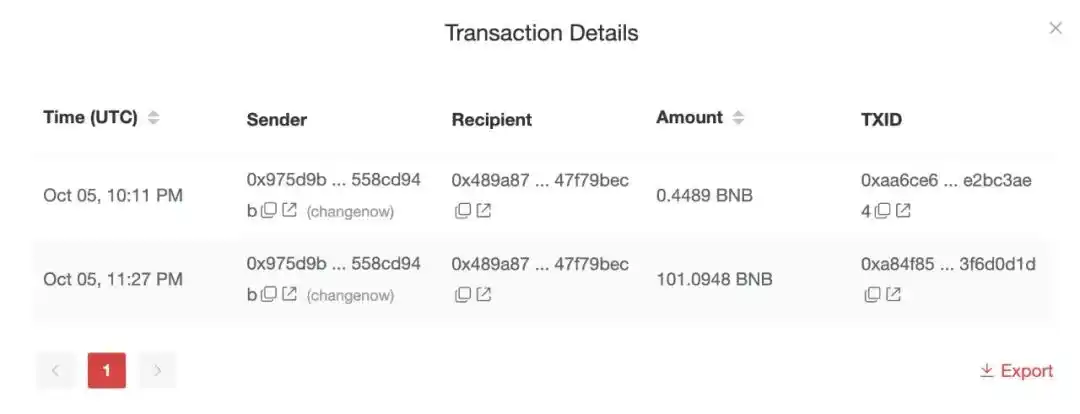
The hacker's address in this attack had interacted with multiple Dapps, These include Multichain, Venus Protocol, Alpaca Finance, Stargate, Curve, Uniswap, Trader Joe's, PancakeSwap, SushiSwap and others. In addition, hackers transferred to ethereum 4.8 million USDT has been blacklisted Tether, AVAX 1.7 million USDT has been blacklisted, Arbitrum 2 million USDT has been blacklisted. Due to the timely suspension of BNB Chain, the hackers' over $410 million in BSC cannot be transferred. On Oct. 8, the hackers transferred about 33,771 new addresses starting with ETH through 0xFA0a3, or about $45 million.
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia
 Related Articles