SlowMist: Vulnerability Analysis of "Zero Yuan Purchase" in TreasureDAO NFT Trading Market
Original title: " "Zero Yuan Purchase" - TreasureDAO NFT Trading Market Vulnerability Analysis "
Original Source: Slow Mist Technology
Original Author: Jiujiu, Slow Mist Security Team
2022 On March 3, according to news from SlowMist, a serious loophole was exposed in the NFT trading market of TreasureDAO. TreasureDAO is an NFT project based on Arbitrum (L2). The project team is currently fixing the vulnerability and promises to provide solutions to affected users. The SlowMist security team immediately intervened in the analysis and shared the results as follows:
Contract address
TreasureMarketplaceBuyer:
0x812cda2181ed7c45a35a691e0c85e231d218e273
TreasureMarketplace:
0x2e3b85f85628301a0bce300dee3a6b04195a15ee
Analysis of vulnerability details
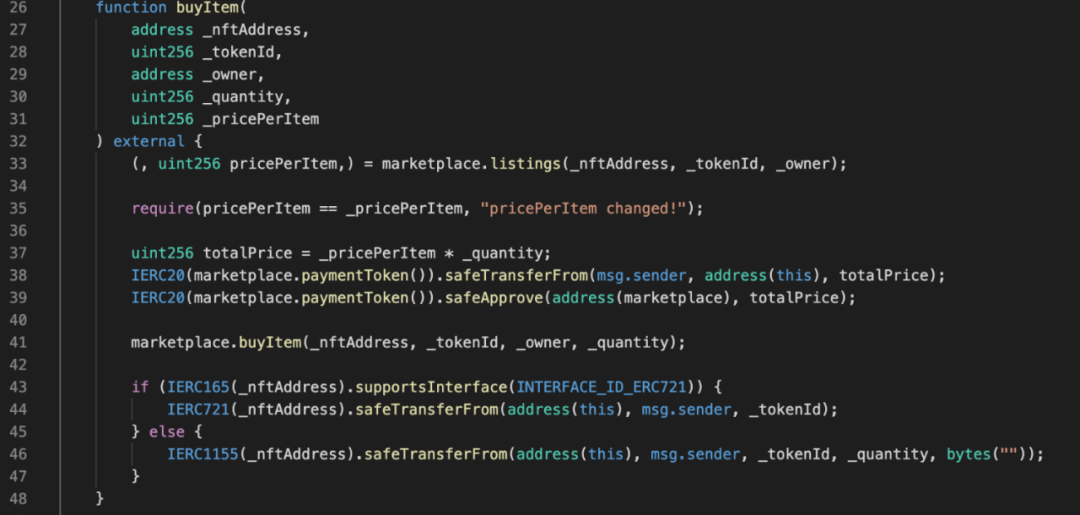
1. The user purchases NFT through the buyItem function in the TreasureMarketplaceBuyer contract. This function will first calculate the total purchase price and enter the Token required for payment into the contract. Then call buyItem in the TreasureMarketplace contract to buy NFT from the market to the TreasureMarketplaceBuyer contract, and then transfer the NFT to the user from the TreasureMarketplaceBuyer contract.
2. In the TreasureMarketplace contract:
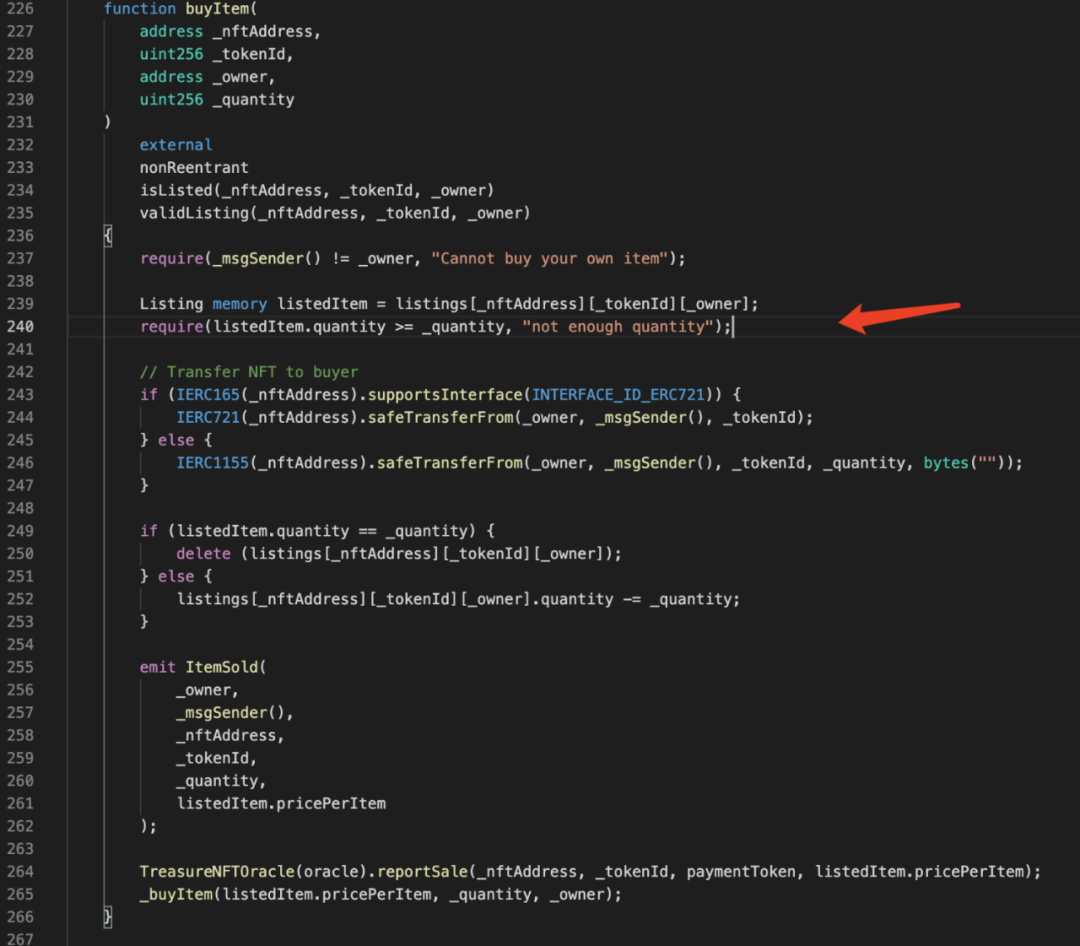
It can be found that if the incoming If the _quantity parameter is 0, you can directly pass require(listedItem.quantity >= _quantity, "not enough quantity"); to check and enter the following transfer NFT process, and there is no NFT transfer of the ERC-721 standard again Quantity judgment, so that although the incoming _quantity parameter is 0, the NFT of the ERC-721 standard can still be transferred. The calculation formula for calculating the purchase price of NFT is totalPrice = _pricePerItem * _quantity, so the purchase price of NFT is calculated as 0, resulting in that all ERC-721 standard NFTs in the market can be purchased for free.
Analysis of attack transactions
Here only shows the details of one attack transaction, and the methods of other attack transactions are the same, so I won’t go into details.
Attack transaction:
https://arbiscan.io/tx /0x82a5ff772c186fb3f62bf9a8461aeadd8ea0904025c3330a4d247822ff34bc02
Attack:
0x4642d9d9a434134cb00 5222ea1422e1820508d7b
Attack details:
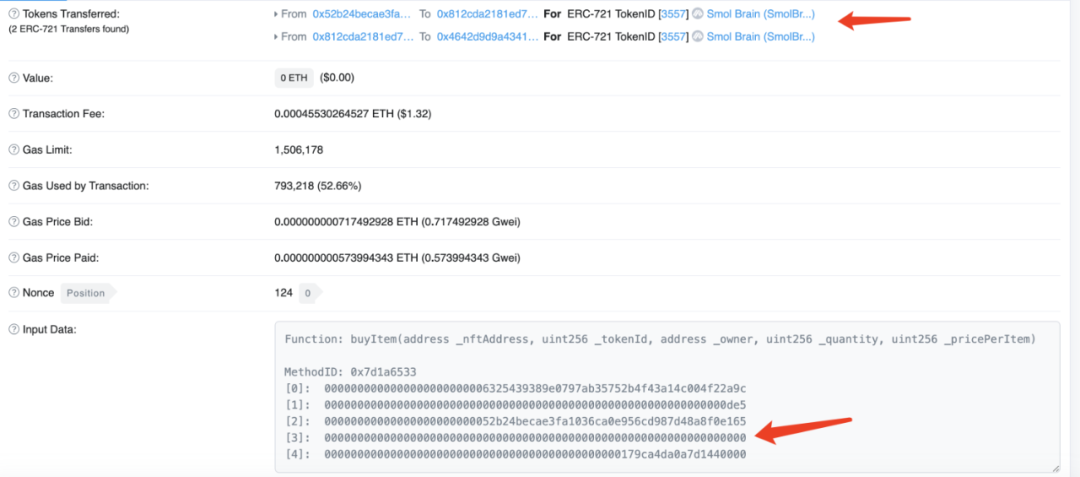
can be viewed from the image below As seen in , the attacker calls the buyItem function in the TreasureMarketplaceBuyer contract and makes the incoming _quantity parameter 0.
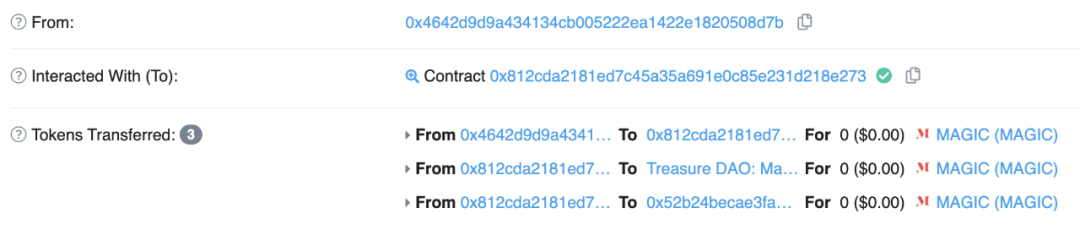
It can be seen that the Token transfer is 0, and the attacker successfully purchased the NFT with tokenID 3557 without paying any cost. The entire attack The process is consistent with what was mentioned in the detailed analysis of the vulnerability above.
Summary
< /p>
The core of this vulnerability is that before the NFT transfer of the ERC-721 standard, it lacks the judgment that the incoming _quantity parameter is not 0, which leads to the ERC-721 standard NFT can be transferred directly and the cost of purchasing NFT is calculated as 0 when calculating the price. In response to such vulnerabilities, the SlowMist security team recommends that before transferring the NFT of the ERC-721 standard, it is necessary to make a good judgment on the incoming quantity to avoid such problems from happening again.
Original link
Welcome to join the official BlockBeats community:
Telegram Subscription Group: https://t.me/theblockbeats
Telegram Discussion Group: https://t.me/BlockBeats_App
Official Twitter Account: https://twitter.com/BlockBeatsAsia

 Related Articles